Root cause
GitHub checked that a pull request's base reference was a branch when creating it, but not consistently when that reference changed. Actions relied on that assumption when deciding which workflows could receive repository secrets and write permissions.
Demonstrated impact
Repository secrets and write authority could become available to an unauthorized workflow.
What to check for
- Check that a pull request's base reference identifies a valid branch whenever it changes and before using it to grant workflow privileges.
- Keep repository secrets confined to explicitly trusted execution contexts.
Award and evidence
How the award was verified, and what the record does not establish
Single finding; the later 2022 follow-up earned USD 7,500 and is excluded.
- Award is reported by the cited source; cash settlement is not independently audited.
Timeline
- Published
- 2021-03-17explicit
- Reported
- 2021-02-04explicit
- Awarded
- 2021-03-03explicit
- Fixed
- 2021-03-02explicit · GitHub Enterprise Server 3.0.1 release; github.com was fixed earlier in February, without an exact final timestamp in the source.
Related visual models
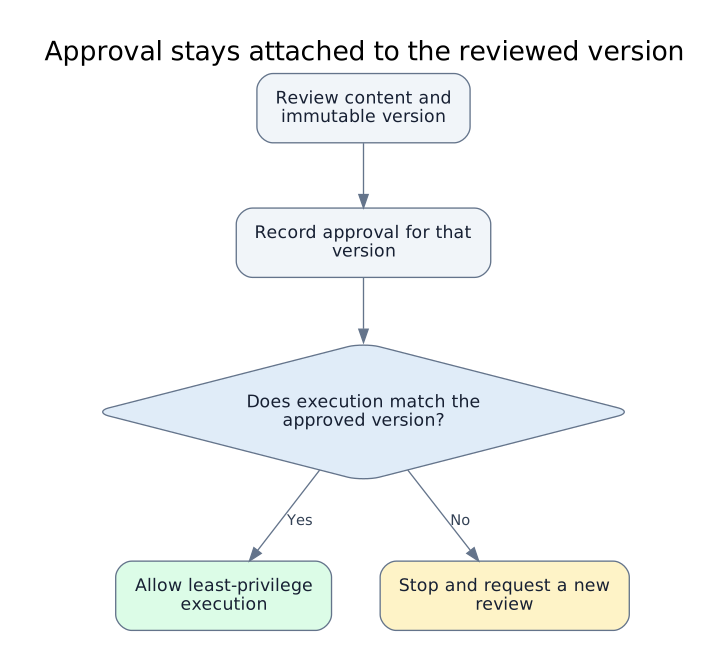
Approval stays attached to the reviewed version
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Related cases
- Angular automation trust and cache isolation weakness
Google · Software supply-chain security · USD 31,337
- GitHub package-source trust allowed dependency confusion
GitHub · Software supply-chain security · USD 20,000
- GitHub runner-image builds shared persistent infrastructure with untrusted workflows
GitHub · Software supply-chain security · USD 20,000
- GitHub comparison output lacked source-repository authorization
GitHub · Authorization and tenant boundaries · USD 10,000
- GitHub unsafe reflection crossed method and credential boundaries
GitHub · Injection and untrusted input · USD 75,000
Sources
- Stealing arbitrary GitHub Actions secretsTeddy Katz · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.