Root cause
The researcher compared the identity available to the approval event with the revision later selected by the build. Approval referred to mutable contribution state without preserving the exact reviewed version. The execution boundary therefore relied on an assumption that the approved and executed content remained identical.
Demonstrated impact
The controlled demonstration executed a newer, unreviewed revision. Access to secrets or cloud resources was a potential consequence of the build’s assigned privileges, not evidence that all pipelines exposed those assets.
Lessons for review
- Bind approval and execution to immutable content identities, with explicit confirmation when the intended revision is ambiguous.
- The researcher’s fix analysis describes check-to-commit binding and explicit commit selection; it does not establish a universal patch recipe.
- Limit build identity privileges and secret availability independently of human approval.
Award and evidence
Older reference: public write-up predates the preferred 12-month window; original report was in 2024.
Re-read the approval model, observed build result, fix analysis and timeline; separated demonstrated behavior, conditional consequences and vendor fix-status confirmation.
- Researcher-reported award; cash settlement was not independently audited.
- The June 18, 2025 status change confirms the issue was marked fixed, not the exact deployment date.
- The public account’s broader security consequences depend on pipeline permissions; no universal secret exposure is established.
Recorded timeline
- Published
- 2025-07-21explicit
- Public Disclosure
- 2025-07-21explicit · Publication of this write-up; earliest disclosure elsewhere was not independently established.
- Reported
- 2024-11-13explicit
- Awarded
- 2025-01-28explicit
Related visual models
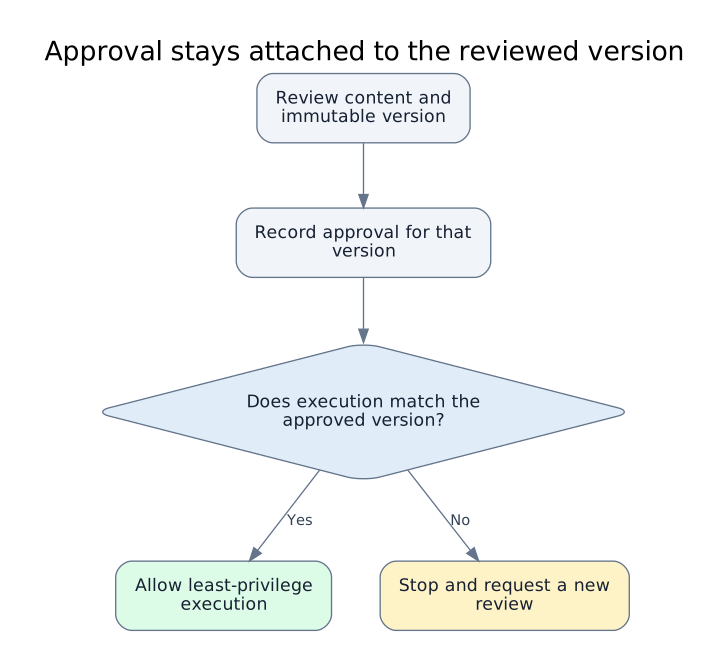
Approval stays attached to the reviewed version
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Sources and provenance
- Who's SHA is it Anyway: Bypassing Google Cloud Build Comment Control for $30,000 Adnan Khan · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot 53796974ace8. Open the complete JSON contract.