Root cause
The account completing sign-in could authorize a different requesting device, and the grant did not preserve the intended client and permissions. The researcher compared the initial approval with the authority of the final token. Cross-device sign-in is expected behavior; the flaw was losing the link to the intended recipient and permissions.
Demonstrated impact
The author reports third-party account access, elevated permissions and mailbox access. Reduced-interaction behavior required a signed-in user opening a link and relevant prior consent. Universal reach, unrestricted persistence and uniform absence of alerts are not independently established.
What to check for
- Preserve one server-side authorization decision across device identity, client identity, subject and permitted actions; every completion path must respect it.
- The researcher recommends server-side grant binding and explicit device confirmation. These are proposed controls, not verified descriptions of the deployed fix.
Award and evidence
How the award was verified, and what the record does not establish
One chain award, counted once. The researcher uses $. USD is inferred from Google’s March 2017 program-wide denomination statement, about nine years before the April 2026 award. That context does not independently establish this individual award’s currency or settlement; cash receipt is unverified.
- No independently reviewed vendor evidence establishes technical reach, award or settlement.
- The March 28, 2026 marked-fixed status does not establish deployment timing or patch contents.
- Specific client permissions, existing consent and downstream token acceptance constrain the reported impact; one broad title does not prove every integration was affected.
Timeline
- Published
- 2026-07-15explicit
- Reported
- 2026-02-25explicit
- Awarded
- 2026-04-02explicit
Related visual models
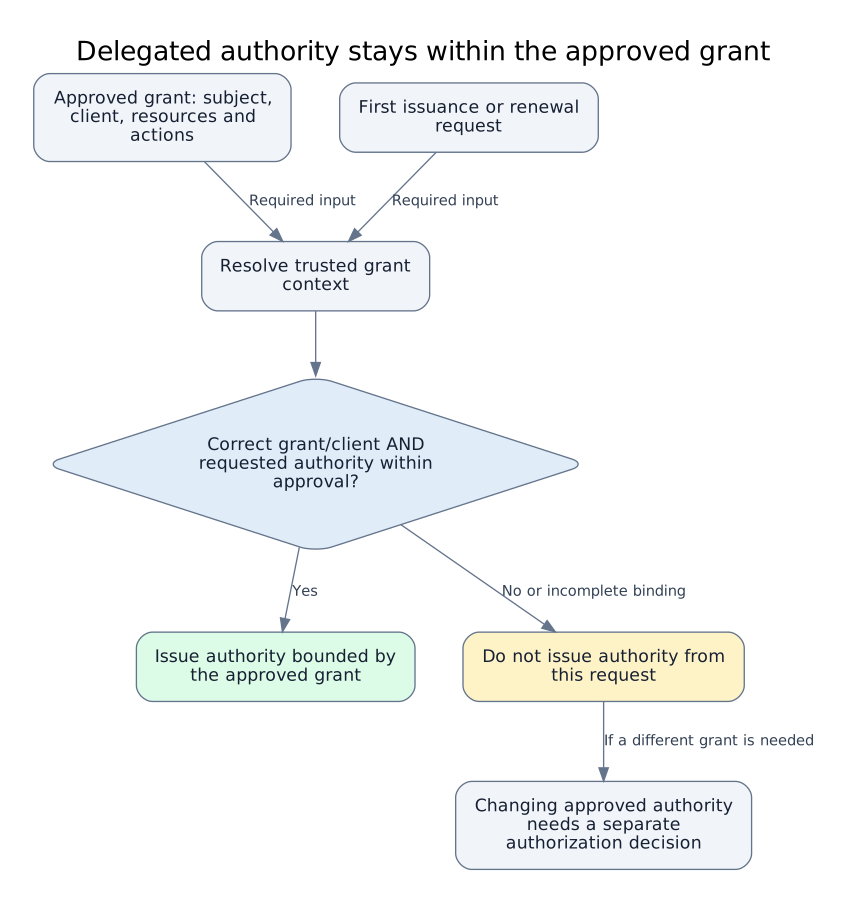
Delegated authority stays within the approved grant
Original editorial defensive synthesis, not a vendor architecture, protocol sequence or independently verified patch. The Google researcher describes lost client and permission binding through a device grant; proposed…
Related cases
- GitLab recovery delivery lacked verified-address binding
GitLab · Authentication and identity · USD 35,000
- LiteSpeed Cache privileged user simulation relied on weak security tokens
LiteSpeed Technologies · Authentication and identity · USD 14,400
- Meta Quest login migration lost OAuth credential confinement
Meta · Authentication and identity · USD 44,250
- Meta account verification weakened linked SMS authentication state
Meta · Authentication and identity · USD 27,200
- Google Mamba temporary outputs lacked access isolation
Google · Authorization and tenant boundaries · USD 37,604.40
- Google Firefly confused worker authority and storage boundaries
Google · Authorization and tenant boundaries · USD 60,000
Sources
- Confused Deputy: Google IdP Universal Account Takeover via Device Code Flow Hijackingweirdmachine64 · reviewed 2026-10-03
- VRP news from NullconGoogle Security Blog · reviewed 2026-10-03
Record reviewed 2026-10-03. Snapshot af2809c308fc. Open the complete JSON contract.