Root cause
Retrieved collaboration content could influence changes to saved memory without the confirmation prompt typically used for other user-data actions. The researcher compared those two paths. Permission to read connected data was being treated as authority to change the user’s lasting assistant state.
Demonstrated impact
In a two-account setup, the researcher confirmed deletion of the test recipient’s saved memories. The scenario required shared-project content access and user-initiated retrieval. Broader cross-tenant access, mailbox compromise and lasting changes to every future response were not demonstrated.
What to check for
- Model persistent memory as a security-sensitive write operation with its own authorization decision.
- Preserve provenance when retrieved content passes between a connector, model and state-changing component.
- Require a trusted authorization signal for each write; permission to summarize content should not imply permission to alter saved preferences.
- Separate observed state changes from speculative downstream behavior in impact reports; the public article does not establish the vendor’s remediation design.
Award and evidence
How the award was verified, and what the record does not establish
The researcher reports being paid $15,000 for this distinct finding; do not combine the separate $1,337 example. Exact award/settlement date is unknown. Dollar-denominated Google bounty; USD normalization. The individual write-up uses the $ symbol rather than spelling out USD.
- No vendor-hosted confirmation of this individual payout found
- Do not confuse this finding with the separate $1,337 memory issue mentioned in the introduction
- Remediation date, exact patch design and current status are not independently established
- The reported demonstration used two researcher-controlled accounts; it does not establish actual customer compromise
Timeline
- Published
- 2026-03-12inferred · DEV article March 12, 2026; the researcher's Reddit write-up is dated March 9, 2026. Original X post is linked but its exact date was not independently established. No exact report, award, or fix dates were found.
- Public Disclosure
- 2026-03-09explicit · Earlier researcher publication on Reddit; linked original X post might be earlier.
Related visual models
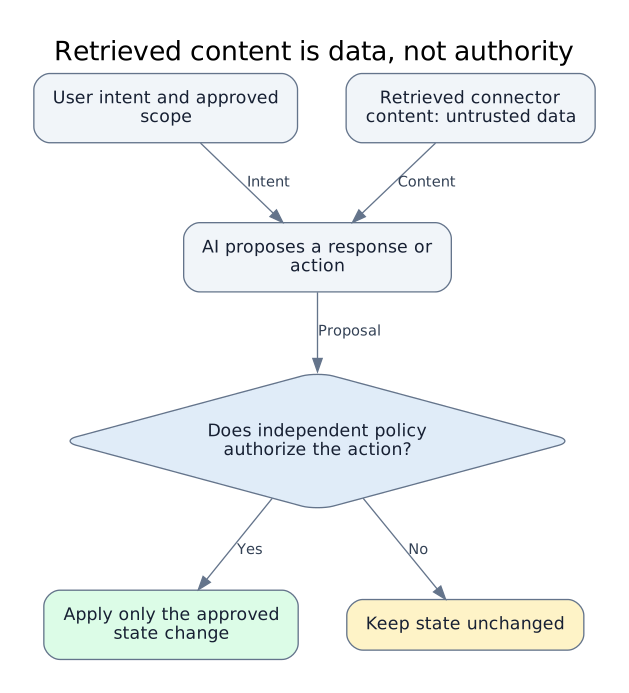
Retrieved content is data, not authority
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Related cases
- Codex metadata collection trusted repository execution helpers
OpenAI · AI integration boundaries · USD 10,000
- Codex automated Git operations trusted repository hook settings
OpenAI · AI integration boundaries · USD 20,000
- Gemini-to-Colab rendering boundary exposed Workspace data
Google · AI integration boundaries · USD 20,000
- Bard Workspace integration weakened output-data boundaries
Google · AI integration boundaries · USD 20,000
- Google Mamba temporary outputs lacked access isolation
Google · Authorization and tenant boundaries · USD 37,604.40
- Google Firefly confused worker authority and storage boundaries
Google · Authorization and tenant boundaries · USD 60,000
Sources
- Google paid me $15,000 for this Prompt Injection bug.Behi · reviewed 2026-10-02
- Supporting primary disclosure sourceBehi · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot a066321c166a. Open the complete JSON contract.