How to use this reference
Review permissions and action boundaries around an owned AI integration; treat filters and model-based checks as partial defenses rather than guarantees.
Before reading
- LLM application and tool-call basics
- Trust boundaries
- An understanding of the application's data and permissions
Context and limits
- Includes attack examples; this collection uses it as a defensive-design reference
- Guidance evolves and individual examples require contextual evaluation
Related visual models
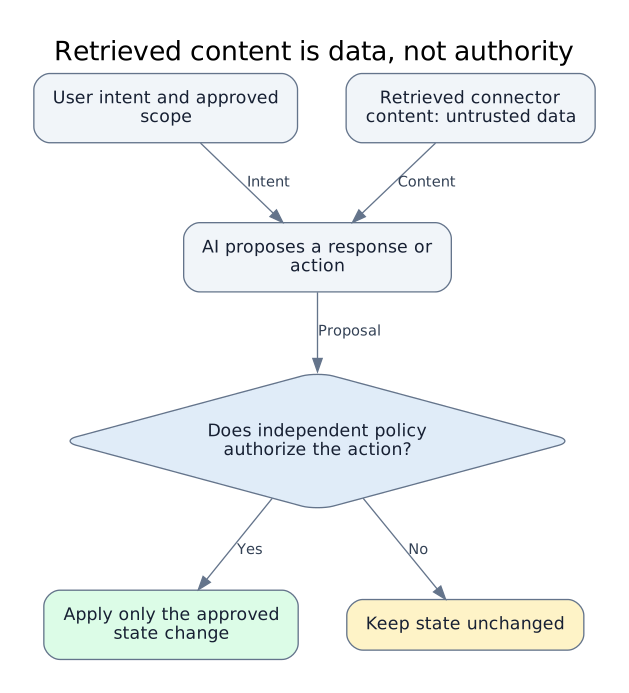
Retrieved content is data, not authority
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Reviewed 2026-10-02
Sources
- LLM Prompt Injection Prevention Cheat SheetOWASP Cheat Sheet Series · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.