Root cause
A workflow did not separate untrusted input from executable instructions. Its build cache was shared with more privileged jobs. Some bot-created pull requests also kept their approvals after their contents changed, weakening the review safeguard.
Demonstrated impact
The researcher demonstrated credential exposure and modeled the remaining path to repository control without executing the final supply-chain modification. Google classified the report as a flagship supply-chain compromise.
What to check for
- Separate caches and artifacts according to trust level.
- Require a new review when bot-created pull requests change, and give automation accounts only the permissions they need.
- Record which impacts were directly demonstrated versus established through design evidence.
Award and evidence
How the award was verified, and what the record does not establish
A Google award email is quoted within the researcher publication; it is not an independently accessed vendor award record. The quote uses only $. USD is a contextual currency inference from the official OSS VRP rules (currency-context), whose Reward amounts section explicitly denominates discretionary bonuses in USD. Those living rules were reviewed on October 3, 2026, after the January 28 award; their wording at award time was not established. They are denomination context only, not proof of this individual award or settlement. No bonus is established or added.
- The reward is an actual award reported in a primary researcher account; payment settlement was not independently audited.
- USD is contextually inferred from later program-level denomination wording, not explicitly stated in the quoted individual award. No conflicting denomination was identified in the reviewed sources.
Timeline
- Published
- 2026-03-03explicit
- Public Disclosure
- 2026-03-03explicit · Publication of this write-up; earliest disclosure elsewhere was not independently established.
- Reported
- 2025-12-11explicit
- Awarded
- 2026-01-28explicit
- Fixed
- 2025-12-21explicit · Researcher timeline says the report was marked fixed on this date; deployment timing and patch effectiveness were not independently verified.
- Mitigated
- 2025-12-12explicit · Researcher timeline records disabling the workflow as mitigation.
Related visual models
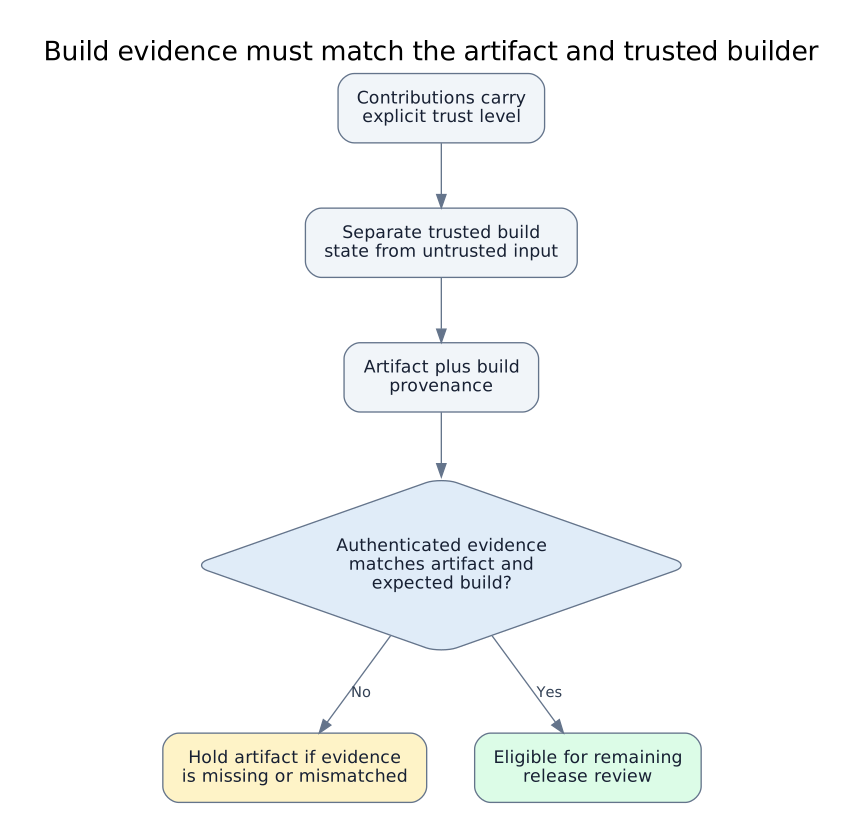
Build evidence must match the artifact and trusted builder
Editorial conceptual model combining the Angular case with SLSA build guidance. The case supports separating automation trust and shared build state; the consumer verification gate is a general design synthesis, not a…
Related cases
- GitHub package-source trust allowed dependency confusion
GitHub · Software supply-chain security · USD 20,000
- GitHub runner-image builds shared persistent infrastructure with untrusted workflows
GitHub · Software supply-chain security · USD 20,000
- GitHub Actions trust depended on invalid repository references
GitHub · Software supply-chain security · USD 25,000
- Google Mamba temporary outputs lacked access isolation
Google · Authorization and tenant boundaries · USD 37,604.40
- Google Firefly confused worker authority and storage boundaries
Google · Authorization and tenant boundaries · USD 60,000
Sources
- Turning Almost Nothing into a Supply Chain Compromise of Angular with GitHub Actions Cache PoisoningAdnan Khan · reviewed 2026-10-03
- Google Open Source Software Vulnerability Reward Program Rules — Reward amountsGoogle · reviewed 2026-10-03
Record reviewed 2026-10-03. Snapshot af2809c308fc. Open the complete JSON contract.