Root cause
The framework accepted request semantics that the controller did not expect. Application logic treated that unexpected case as permission to grant access, even though the usual consent checks did not apply. The researcher found the mismatch by comparing the consent screen’s intended action with routing and controller behavior. Every new grant should have required explicit, validated user approval.
Demonstrated impact
The researcher reports that a user visiting a malicious website could unintentionally grant an application access to read or modify private GitHub data. This demonstrates unauthorized delegated access, rather than evidence that the attacker learned the account password or that all unrelated account controls failed.
What to check for
- Require positive validation of the intended state-changing operation; reject unrecognized alternatives rather than defaulting to a privileged action.
- Model framework routing, request interpretation and consent enforcement as separate layers whose assumptions must agree.
- Verify that consent and request-integrity checks remain attached to every path that creates a grant.
- The source dates the production fix and later Enterprise releases, but does not document the exact patch here; these lessons are defensive recommendations.
Award and evidence
How the award was verified, and what the record does not establish
Individual report; production fix date is for github.com, with enterprise releases following June 26. The researcher uses $ without an explicit currency. USD is a contextual inference from github-currency-context-2017: GitHub's January 9, 2017 program article, updated June 25, 2021, explicitly names USD. Its publication predates the June 26, 2019 award and its displayed update postdates it; this is non-contemporaneous program-wide context, not proof of this individual award's currency or settlement. No conflicting denomination was found in the reviewed sources.
- Researcher-reported award; cash settlement is not independently audited.
- The reported impact requires user interaction. Exact vendor patch implementation and evidence of real-world abuse are not supplied.
- USD is inferred from a program-wide article published in 2017 and updated in 2021, not contemporaneous individual-award evidence from 2019. The reviewed sources do not independently establish this award's denomination or cash settlement; payment date remains unknown.
Timeline
- Published
- 2019-11-05explicit
- Reported
- 2019-06-19explicit
- Awarded
- 2019-06-26explicit
- Fixed
- 2019-06-20explicit
Related visual models
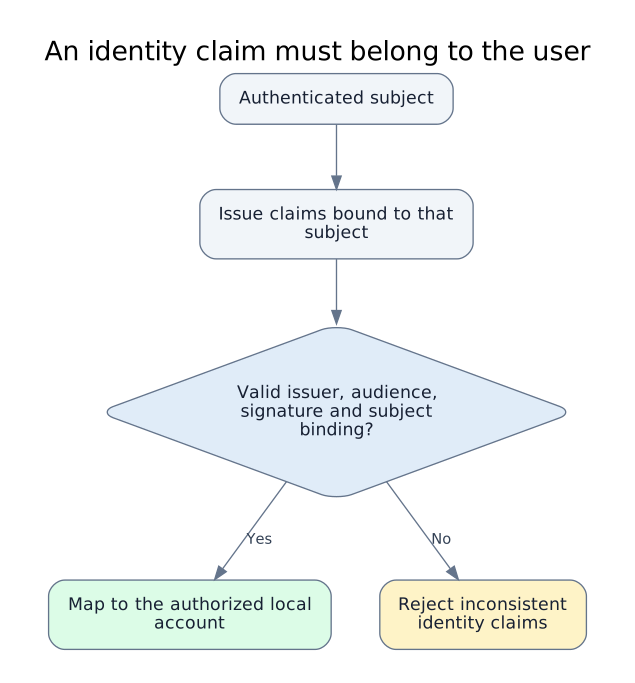
An identity claim must belong to the user
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Related cases
- Google Mamba temporary outputs lacked access isolation
Google · Authorization and tenant boundaries · USD 37,604.40
- Google Firefly confused worker authority and storage boundaries
Google · Authorization and tenant boundaries · USD 60,000
- Google Application Integration mixed resource and service authority
Google · Authorization and tenant boundaries · USD 75,000
- Google support API exposed customer and agent data
Google · Authorization and tenant boundaries · USD 14,337
- GitHub package-source trust allowed dependency confusion
GitHub · Software supply-chain security · USD 20,000
- GitHub unsafe reflection crossed method and credential boundaries
GitHub · Injection and untrusted input · USD 75,000
Sources
- Bypassing GitHub’s OAuth flowTeddy Katz · reviewed 2026-10-05
- Bug Bounty anniversary promotion: bigger bounties in January and FebruaryNeil Matatall · reviewed 2026-10-05
Record reviewed 2026-10-05. Snapshot af2809c308fc. Open the complete JSON contract.