vulns.co
/
GKData.io MCP

Conceptual model · 1 min read

An identity claim must belong to the user

Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.

The conceptual model
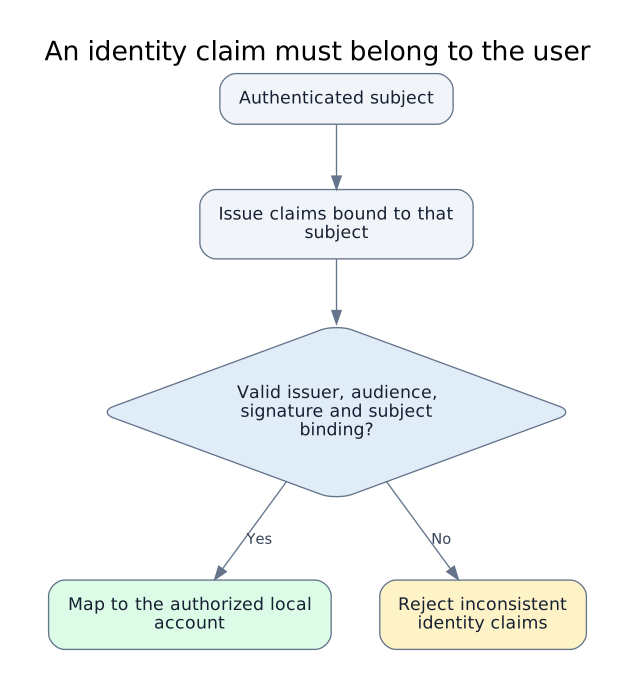
The identity provider authenticates a subject and binds issued claims to it. The relying application validates the issuer, audience, signature, and ownership binding before mapping to a local account. Failed validation is rejected.

Cases and references behind the model

Sources and provenance

  1. bhavukjain.com Primary source
  2. blog.teddykatz.com Primary source
  3. www.rfc-editor.org Primary source

Record reviewed 2026-10-02. Snapshot 53796974ace8. Open the complete JSON contract.

GitHub snapshot 2026-10-04

53796974ace8 · JSON exports & schemas · CC BY 4.0 content / MIT software