How to use this reference
Compare an owned integration's documented design against the standard and record deviations and compensating controls.
Before reading
- OAuth roles and authorization flows
- HTTP redirects and TLS
- Basic token and session concepts
Context and limits
Related visual models
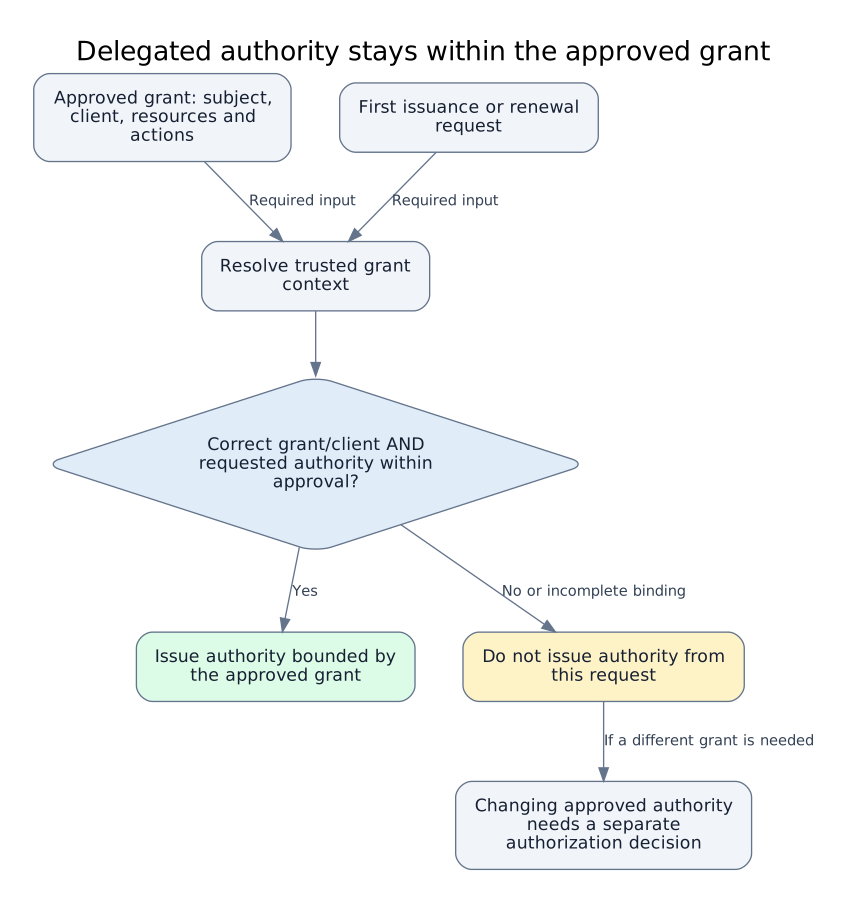
Delegated authority stays within the approved grant
Original editorial defensive synthesis, not a vendor architecture, protocol sequence or independently verified patch. The Google researcher describes lost client and permission binding through a device grant; proposed…
Reviewed 2026-10-04
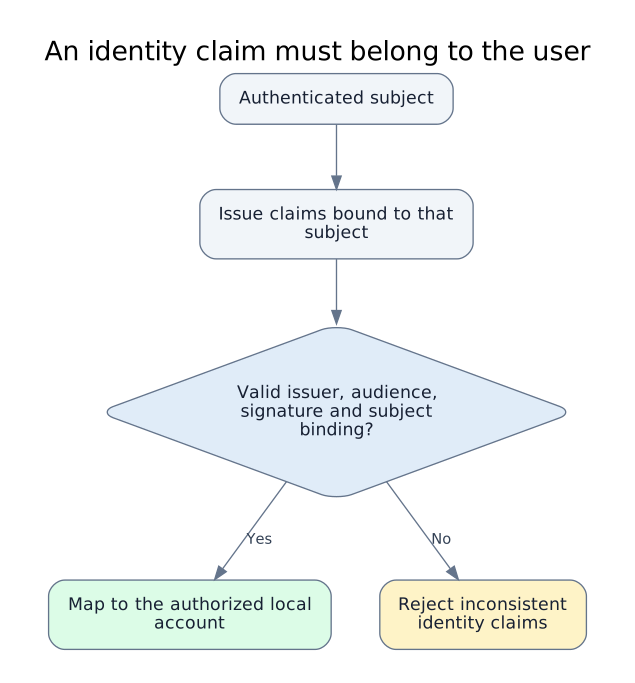
An identity claim must belong to the user
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Reviewed 2026-10-02
Sources
- RFC 9700: Best Current Practice for OAuth 2.0 SecurityInternet Engineering Task Force / RFC Editor · reviewed 2026-10-02
- RFC 9700: Best Current Practice for OAuth 2.0 SecurityInternet Engineering Task Force / RFC Editor · reviewed 2026-10-06
Record reviewed 2026-10-06. Snapshot af2809c308fc. Open the complete JSON contract.