vulns.co
/
GKData.io MCP and API Buy me a coffee

Security theme

Software supply-chain security

Build systems, package provenance, release integrity, and automation trust. 6 disclosures · 7 related references · 2 diagrams.

Disclosures

Related learning

GitHub Architecture Guide

GitHub Artifact Attestations: Provenance and Consumer Policy

GitHub's guide explains what signed artifact attestations say about a build, including its workflow, repository, organization, environment, commit, triggering event and OIDC identity information. Consumers use those…

Reviewed 2026-10-12

National Institute of Standards and Technology Architecture Guide

NIST SP 800-190: Application Container Security Guide

NIST's container security guide explains the risks of sharing an operating-system kernel and the need to separate workloads and limit runtime permissions. It covers images, registries, orchestration, runtimes and hosts,…

Reviewed 2026-10-02

NIST Implementation Guide

NIST SSDF 1.1: Component Governance and Release Provenance

NIST's SSDF 1.1 describes how to select, maintain and assess software components throughout their use. Practices PW.4.1 and PW.4.4 cover organizational requirements, component integrity, vulnerabilities and maintenance…

Reviewed 2026-10-12

OWASP Cheat Sheet Series Implementation Guide

Authorization Cheat Sheet

OWASP recommends granting only needed permissions, denying access by default and making consistent authorization decisions on every request. The guidance also covers failure handling, logging and regression tests for…

Reviewed 2026-10-02

OWASP Cheat Sheet Series Implementation Guide

OWASP Transaction Authorization

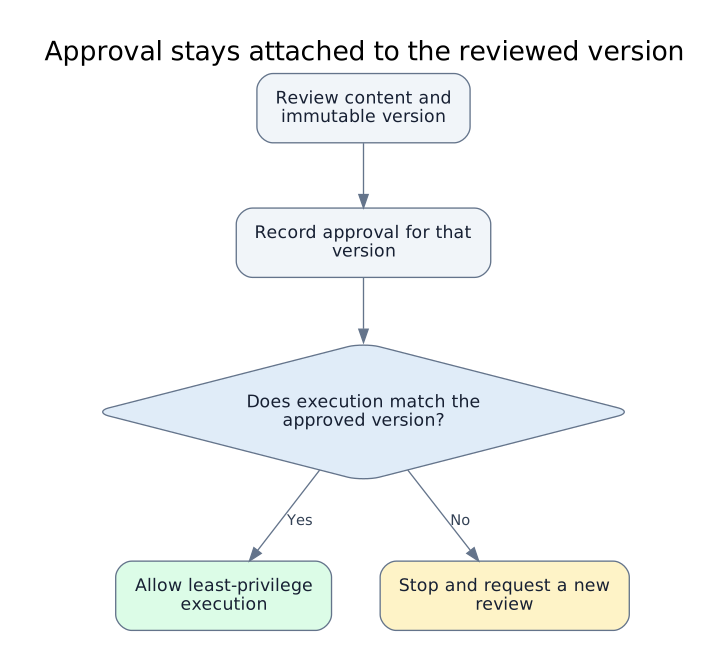
OWASP explains how to tie approval to a specific operation and its important details. Applications must preserve the approved data, enforce valid workflow steps and check authorization again when the operation runs.

Reviewed 2026-10-02

Sigstore Architecture Guide

Sigstore Security Model

Sigstore's security guide explains how software signatures link an artifact to a signing identity and an auditable history. It describes identity issuers, Fulcio's short-lived certificates, trusted roots and Rekor's…

Reviewed 2026-10-12

SLSA Community Security Standard

SLSA v1.2: supply-chain security and build provenance

SLSA v1.2 defines separate assurance tracks for source code and builds. Its build track moves from recording how an artifact was produced to authenticated hosted builds and stronger isolation, helping consumers check…

Reviewed 2026-10-02

Visual models

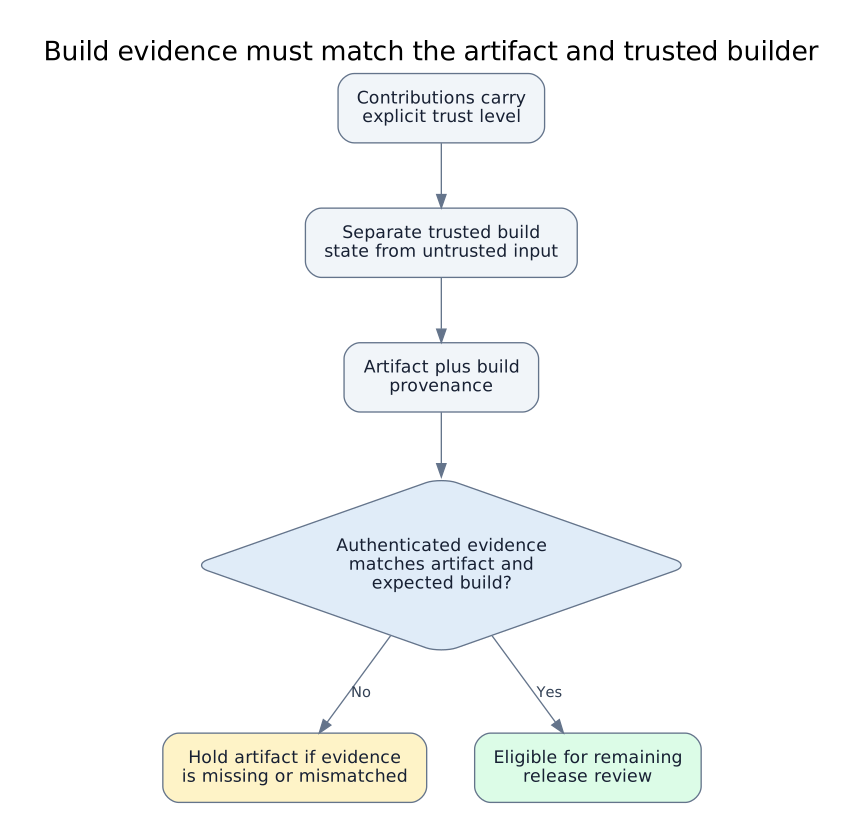
Untrusted contributions remain separated from trusted build state. An artifact and its provenance reach a consumer policy gate. Only authenticated evidence matching the artifact and expected builder and inputs makes it eligible for release review; missing or mismatched evidence prevents promotion.

Conceptual model Diagram

Build evidence must match the artifact and trusted builder

Editorial conceptual model combining the Angular case with SLSA build guidance. The case supports separating automation trust and shared build state; the consumer verification gate is a general design synthesis, not a…

Reviewed 2026-10-03

Related learning follows the topic crosswalk or an explicit diagram relationship. It does not classify a resource as a finding. Topics overlap, so their counts should not be added together.

Library synced 2026-11-18 · cases last reviewed 2026-10-05

af2809c308fc · JSON exports & schemas · CC BY 4.0 content / MIT software