vulns.co
/
GKData.io MCP and API Buy me a coffee

Vulnerability family

Server-side request trust

Destination validation and boundaries in server-initiated requests. 1 disclosures · 1 related references · 1 diagrams.

Disclosures

Related learning

OWASP Cheat Sheet Series Implementation Guide

OWASP Server-Side Request Forgery Prevention

OWASP explains how destination checks and network isolation constrain requests made by a server. The guidance distinguishes services that contact a fixed set of trusted destinations from those that need broader external…

Reviewed 2026-10-07

Visual models

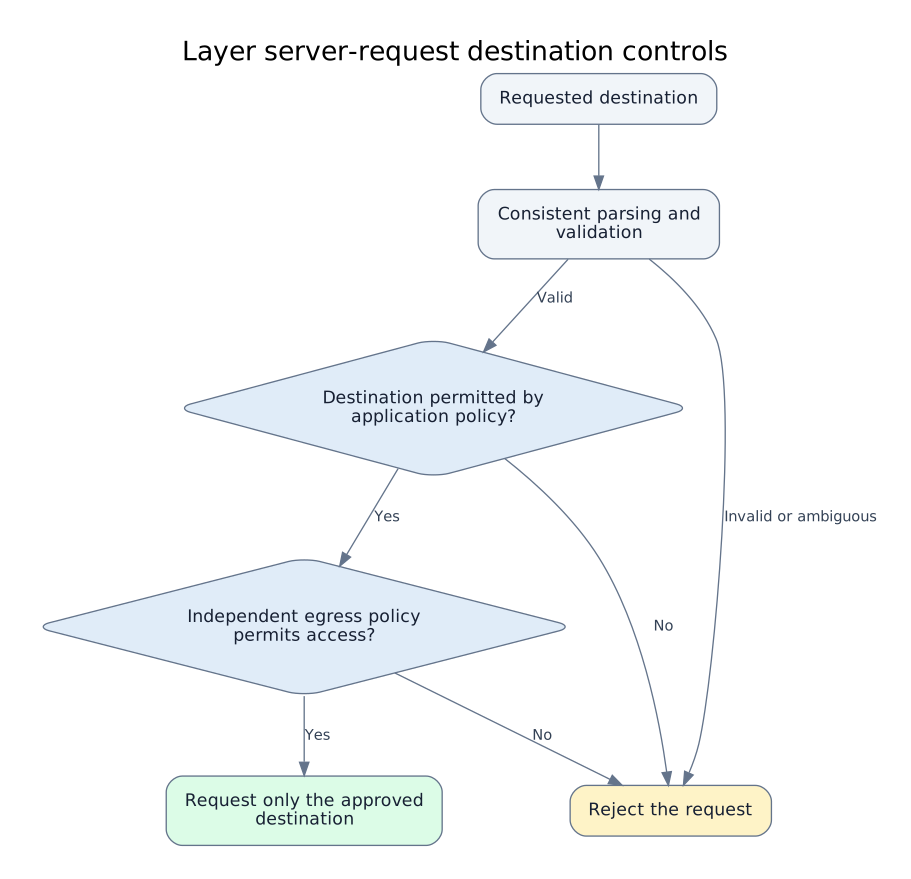
A requested destination passes consistent parsing, application policy and independent network egress checks. Invalid input or either policy failure is rejected. Only an approved destination is requested.

Conceptual model Diagram

Layer server-request destination controls

Original conceptual defense-in-depth model linked to the historical Shopify Exchange case and OWASP guidance. It is not a vendor architecture diagram. Policy must fit the service’s destination requirements.

Reviewed 2026-10-02

Related learning follows the topic crosswalk or an explicit diagram relationship. It does not classify a resource as a finding. Topics overlap, so their counts should not be added together.

Library synced 2026-11-18 · cases last reviewed 2026-10-05

af2809c308fc · JSON exports & schemas · CC BY 4.0 content / MIT software