Root cause
Server-side fetching crossed the boundary between externally influenced screenshot work and internal infrastructure. The vendor’s remediation targeted metadata access and internal destinations; its retrospective omits authentication prerequisites and the researcher’s reasoning process.
Demonstrated impact
Shopify confirms reported root-access capability across containers in the affected subset, explicitly excluding Shopify core. The retrospective does not establish compromise of every container or quantify exposed data. The service was disabled within an hour; infrastructure review preceded metadata shielding and internal-address restrictions.
What to check for
- Separately enforce request-destination policy, workload privilege and infrastructure segmentation; each limits a different boundary.
- Treat metadata as privileged infrastructure data and deny unneeded service access.
- Preserve the distinction between a demonstrated access capability and a claim of widespread compromise.
Award and evidence
How the award was verified, and what the record does not establish
Vendor retrospective explicitly ties this amount to one report. Original report, award, and fix dates are not supplied.
- The publication date is retrospective, not the original discovery date.
- Underlying report details were not independently reread; no additional exploit prerequisites or investigative chronology are asserted.
Timeline
- Published
- 2019-04-03explicit
Related visual models
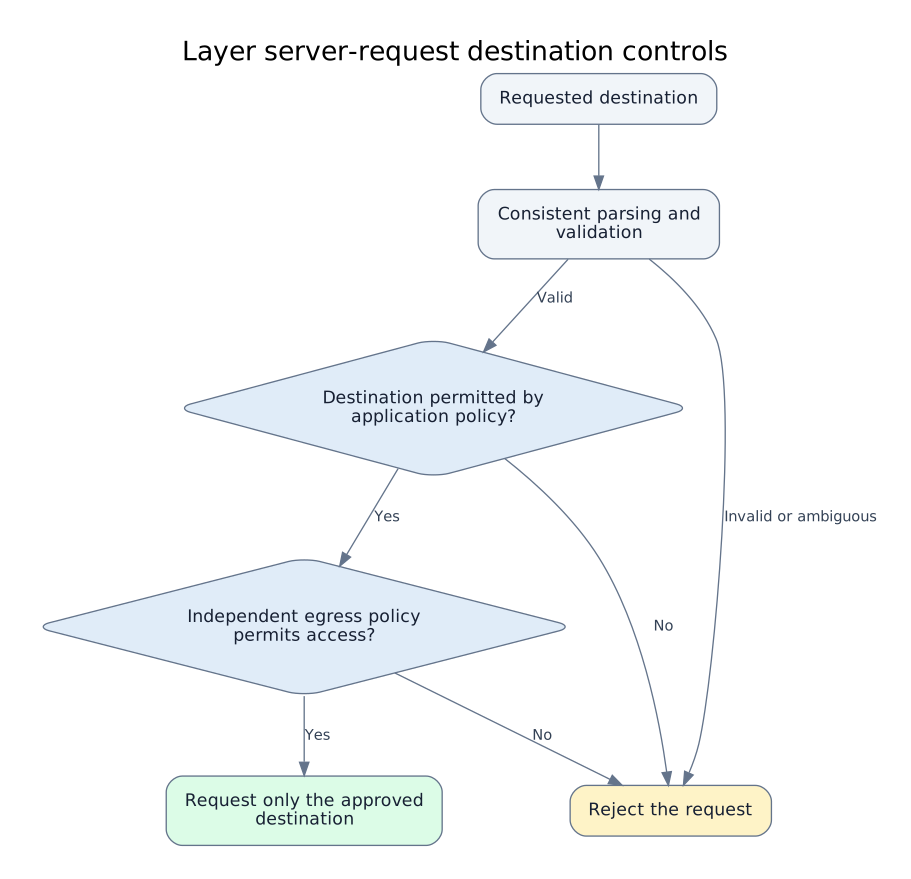
Layer server-request destination controls
Original conceptual defense-in-depth model linked to the historical Shopify Exchange case and OWASP guidance. It is not a vendor architecture diagram. Policy must fit the service’s destination requirements.
Related cases
- Shopify automatic account conversion lost merchant-consent binding
Shopify · Authorization and tenant boundaries · USD 20,000
Sources
- One Million Dollars in Bug BountiesPeter Yaworski / Shopify · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.