The conceptual model
Cases and references behind the model
Sources
- shopify.engineeringPrimary source
- cheatsheetseries.owasp.orgPrimary source
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.
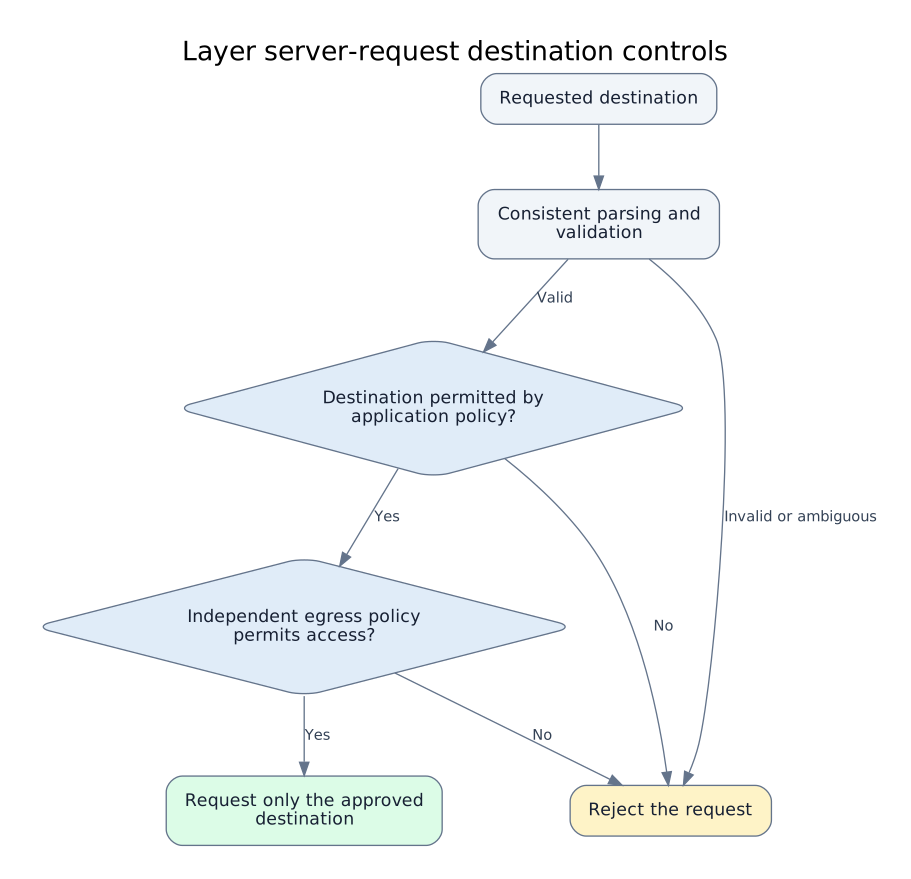
Original conceptual defense-in-depth model linked to the historical Shopify Exchange case and OWASP guidance. It is not a vendor architecture diagram. Policy must fit the service’s destination requirements.
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.
Library synced 2026-11-18 · cases last reviewed 2026-10-05
af2809c308fc · JSON exports & schemas · CC BY 4.0 content / MIT software
| / | Focus search on this page |
| Ctrl K | Search everything (command palette) |
| 1-9 | Library, Generator, Playbooks, Gadgets, Checklists, Payloads, Bypasses, Utilities, Reports |
| 0 | AI / MCP connector |
| j / k | Move selection down / up |
| Enter | Expand / open selected |
| c | Copy primary command of selected |
| f | Toggle favorite on selected tool |
| Esc | Clear search / close |