How to use this reference
Review owned-service destination policy, parser consistency, redirect behavior and independent egress restrictions.
Before reading
- Basic knowledge of web requests and application/network boundaries
Context and limits
- The destination-policy design depends on business requirements. Metadata protections complement application validation and network isolation.
- A permitted domain name or a separate DNS review does not by itself establish an authorized connection destination. The client's actual connection must remain restricted to addresses validated against the application's destination policy.
- Keep that destination policy effective for retry and fallback connections. DNS configuration and monitoring add detection but do not replace enforcement when a connection is made.
Related visual models
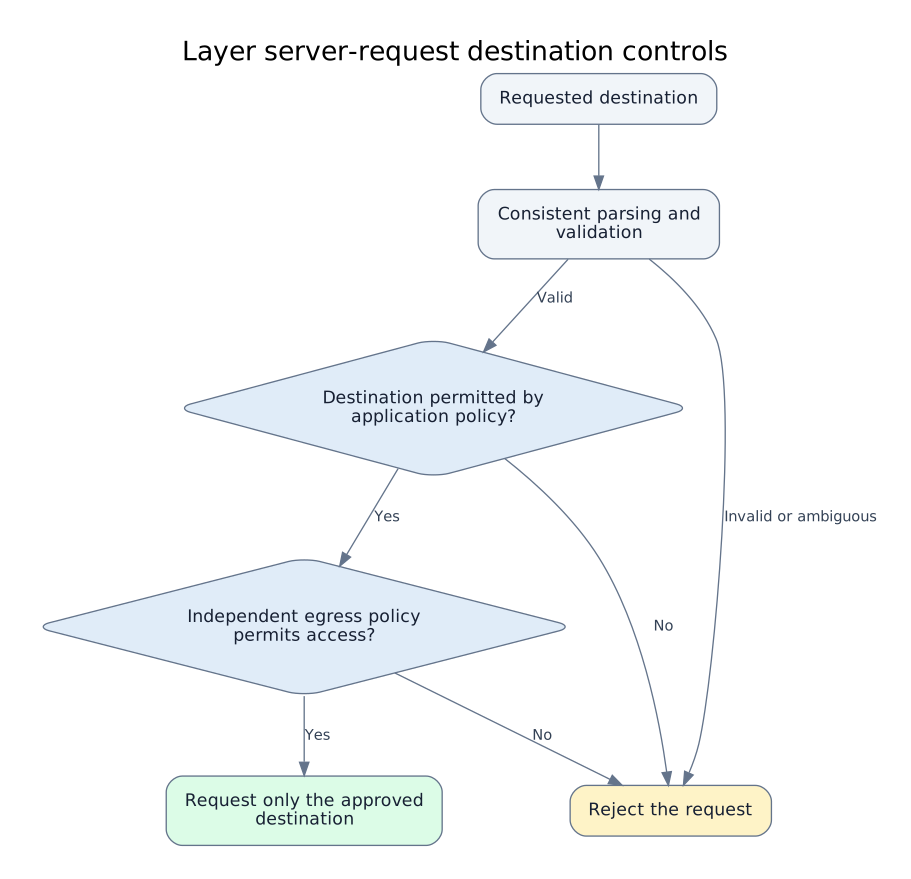
Layer server-request destination controls
Original conceptual defense-in-depth model linked to the historical Shopify Exchange case and OWASP guidance. It is not a vendor architecture diagram. Policy must fit the service’s destination requirements.
Reviewed 2026-10-02
Sources
- Server-Side Request Forgery Prevention Cheat SheetOWASP · reviewed 2026-10-02
- Server-Side Request Forgery Prevention Cheat Sheet: Domain nameOWASP Cheat Sheet Series · reviewed 2026-10-07
Record reviewed 2026-10-07. Snapshot af2809c308fc. Open the complete JSON contract.