vulns.co
/
GKData.io MCP and API Buy me a coffee

Vulnerability family

Injection and untrusted input

Separation between untrusted data and executable interpretation. 13 disclosures · 16 related references · 3 diagrams.

Disclosures

Related learning

Django Software Foundation Maintainer Advisory

Django: ORM alias metadata must not acquire query authority

Django's CVE-2026-1312 advisory describes column aliases being interpreted as SQL structure when combined with relation filtering and ordering. Exposure requires an application to accept untrusted alias definitions in…

Reviewed 2026-10-03

DOMPurify / Cure53 Maintainer Advisory

DOMPurify: accepted DOM realms must retain complete sanitization

DOMPurify could accept DOM objects from another JavaScript realm but fail to recognize them during later sanitization. Its CVE-2026-49458 advisory describes local-constructor checks that could skip protections and leave…

Reviewed 2026-10-04

SBA Research Research Paper

Laravel: preserve output encoding in debug diagnostics

Laravel's debug error page could render request-derived route values without HTML encoding. SBA Research's CVE-2024-13919 advisory demonstrates browser script execution in a minimal application. The lesson is that data…

Reviewed 2026-10-05

zhero_web_security Research Paper

Next.js: response metadata must preserve representation boundaries

Researchers report stored browser script execution in an anonymized production Next.js application with unusual middleware header copying and an external shared cache. Client-supplied metadata changed how the browser…

Reviewed 2026-10-04

OWASP Cheat Sheet Series Implementation Guide

Authorization Cheat Sheet

OWASP recommends granting only needed permissions, denying access by default and making consistent authorization decisions on every request. The guidance also covers failure handling, logging and regression tests for…

Reviewed 2026-10-02

OWASP Cheat Sheet Series Implementation Guide

HTML5 Security Cheat Sheet: Web Messaging

OWASP explains how to check a browser message's origin and format and handle its contents as data. These are separate controls: verifying the sender does not replace validating the message or handling its content safely.

Reviewed 2026-10-02

OWASP Cheat Sheet Series Architecture Guide

LLM Prompt Injection Prevention Cheat Sheet

OWASP recommends layered defenses for LLM applications that read untrusted content or use tools. The guidance covers tracking data sources, limiting permissions, authorizing actions and monitoring behavior, while…

Reviewed 2026-10-02

Python Software Foundation Implementation Guide

Python subprocess: executable, argument, and interpreter boundaries

Python's documentation distinguishes the executable being launched, its arguments and any shell that interprets them. Python does not implicitly choose a shell, but Windows may launch batch files through one. The shlex…

Reviewed 2026-10-03

SLSA Community Security Standard

SLSA v1.2: supply-chain security and build provenance

SLSA v1.2 defines separate assurance tracks for source code and builds. Its build track moves from recording how an artifact was produced to authenticated hosted builds and stronger isolation, helping consumers check…

Reviewed 2026-10-02

Trix maintainers Maintainer Advisory

Trix: validate stored attachment data before link interpretation

Trix could turn stored attachment metadata into an unsafe browser link without checking its meaning when rendered. The maintainer describes stored cross-site scripting that requires control over that metadata, later…

Reviewed 2026-10-05

Visual models

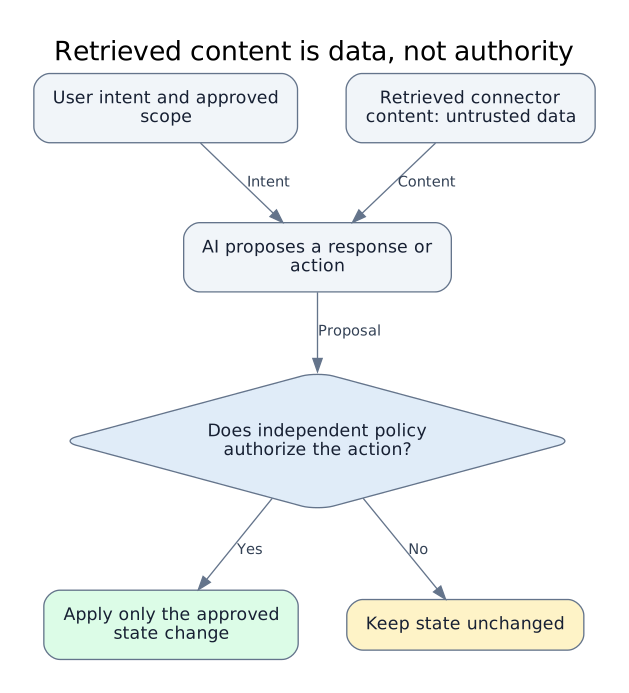
User intent and untrusted connector content enter the AI workflow separately. A proposed action reaches an independent policy decision. Only an authorized state change proceeds; otherwise state remains unchanged.

Conceptual model Diagram

Retrieved content is data, not authority

Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.

Reviewed 2026-10-02
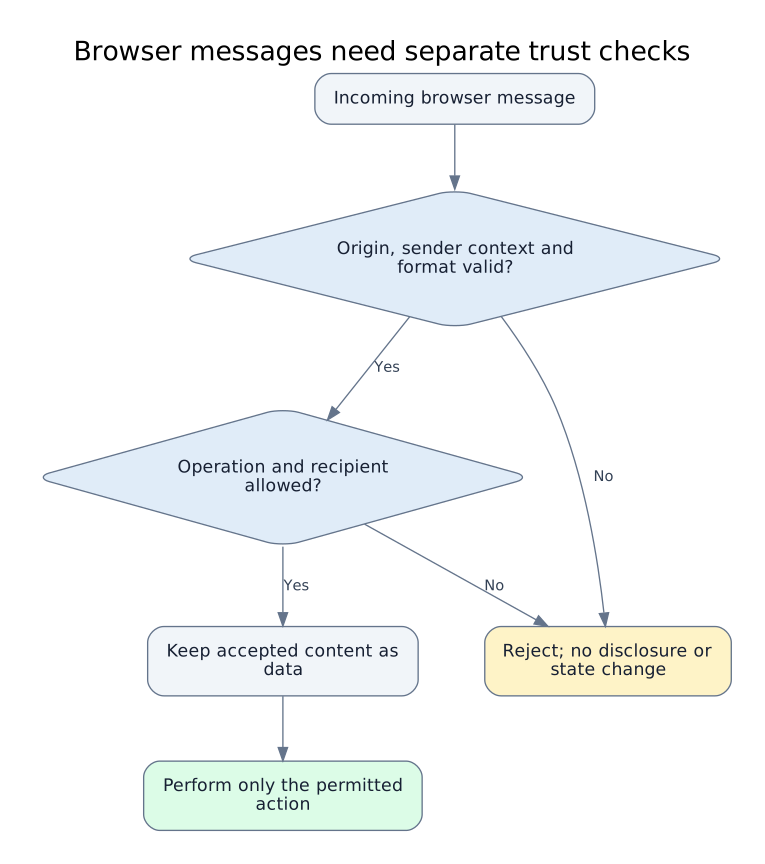
An incoming browser message first passes origin, sender-context and format validation. A separate decision checks the operation and recipient. Failed checks reject the message without disclosure or state change. Approved content remains data and only the permitted action is performed.

Conceptual model Diagram

Browser messages need separate trust checks

Original defensive model combining OWASP messaging and authorization guidance with the linked historical cases. These are independent design checks, not a vendor patch diagram or an operational reproduction.

Reviewed 2026-10-02
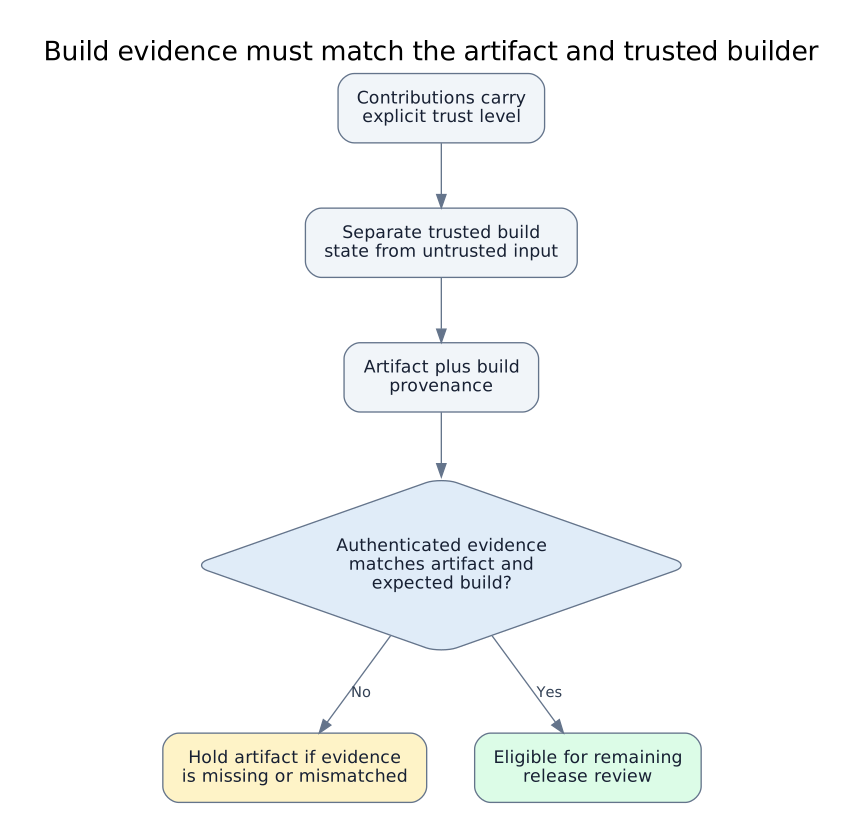
Untrusted contributions remain separated from trusted build state. An artifact and its provenance reach a consumer policy gate. Only authenticated evidence matching the artifact and expected builder and inputs makes it eligible for release review; missing or mismatched evidence prevents promotion.

Conceptual model Diagram

Build evidence must match the artifact and trusted builder

Editorial conceptual model combining the Angular case with SLSA build guidance. The case supports separating automation trust and shared build state; the consumer verification gate is a general design synthesis, not a…

Reviewed 2026-10-03

Related learning follows the topic crosswalk or an explicit diagram relationship. It does not classify a resource as a finding. Topics overlap, so their counts should not be added together.

Library synced 2026-11-18 · cases last reviewed 2026-10-05

af2809c308fc · JSON exports & schemas · CC BY 4.0 content / MIT software