vulns.co
/
GKData.io MCP and API Buy me a coffee

Conceptual model

Browser messages need separate trust checks

Original defensive model combining OWASP messaging and authorization guidance with the linked historical cases. These are independent design checks, not a vendor patch diagram or an operational reproduction.

The conceptual model
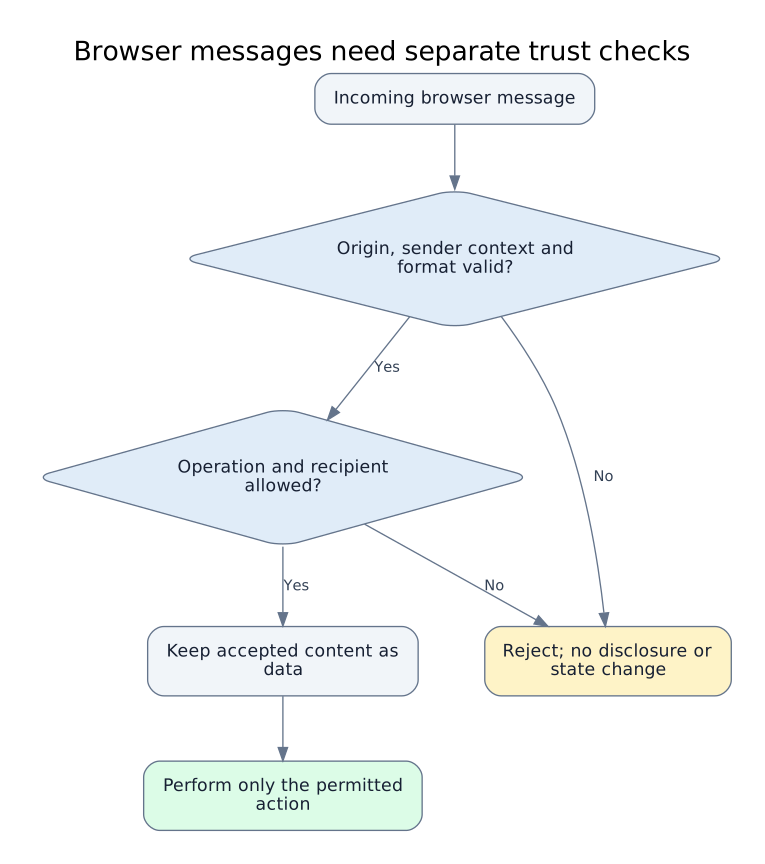
An incoming browser message first passes origin, sender-context and format validation. A separate decision checks the operation and recipient. Failed checks reject the message without disclosure or state change. Approved content remains data and only the permitted action is performed.

Cases and references behind the model

Sources

  1. cheatsheetseries.owasp.orgPrimary source
  2. cheatsheetseries.owasp.orgPrimary source
  3. ysamm.comPrimary source
  4. ysamm.comPrimary source

Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.

Library synced 2026-11-18 · cases last reviewed 2026-10-05

af2809c308fc · JSON exports & schemas · CC BY 4.0 content / MIT software