Root cause
A trusted-origin check was treated as a complete access decision. It did not bind the requested operation and recipient to the page data being protected. By tracing browser messages into requests containing page context, the researcher found that sensitive information could pass into a request associated with a different identity.
Demonstrated impact
The researcher reports authorization-material exposure and consequent Instagram takeover with user interaction. Wider script deployment does not establish equivalent impact on every embedding site or evidence of real-world abuse.
What to check for
- Check the expected sender relationship and message structure, then independently authorize the requested operation and recipient.
- Define a minimal disclosure contract for analytics and integration messages; omit authentication artifacts from general page context.
- Review grant-to-client binding separately from message transport and preserve those distinctions in evidence.
- These are defensive recommendations; the precise vendor patch and the separately alleged grant-binding fix are not independently verified.
Award and evidence
How the award was verified, and what the record does not establish
One researcher-reported bug bounty, not an event total. The article uses $; prior official Meta program reporting supplies USD context. Actual cash settlement is not established.
- Researcher-reported award; no independent vendor confirmation or audited transfer.
- January 2026 page dates may reflect publication or archive migration; original disclosure is not established.
- USD normalization uses earlier official program context rather than an award receipt.
- A separate grant-binding flaw is alleged and described as disputed; vendor confirmation and its precise fix date are unverified.
Timeline
- Reported
- 2024-10-16explicit
- Awarded
- 2025-02-12explicit
- Fixed
- 2024-10-24explicit · Overall fix date in the researcher timeline. A separately alleged, disputed grant-binding component has no confirmed fix date; this timestamp does not cover it.
Related visual models
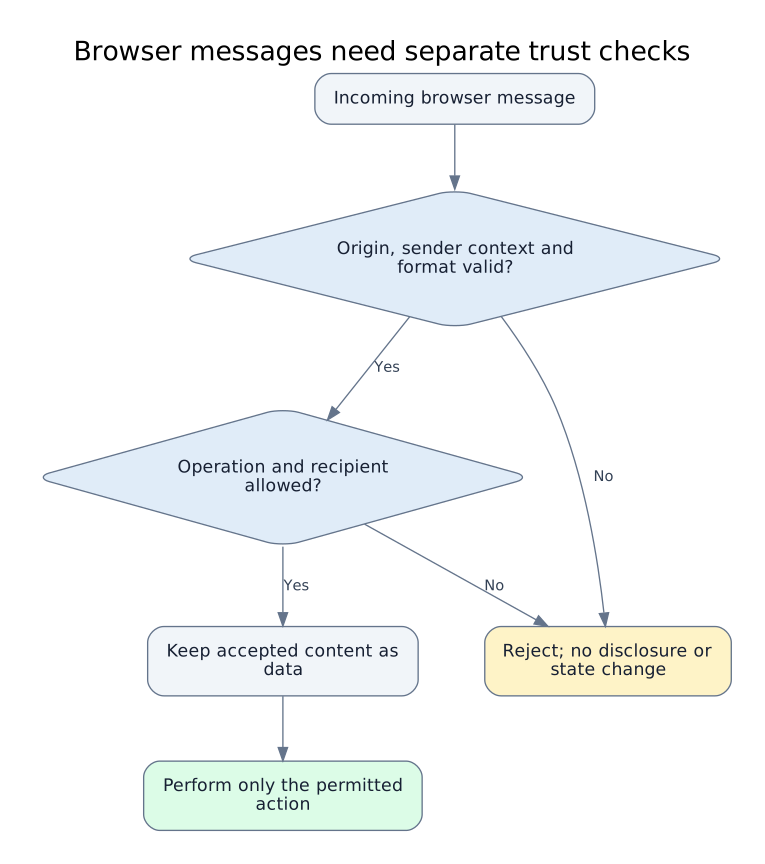
Browser messages need separate trust checks
Original defensive model combining OWASP messaging and authorization guidance with the linked historical cases. These are independent design checks, not a vendor patch diagram or an operational reproduction.
Related cases
- Google Mamba temporary outputs lacked access isolation
Google · Authorization and tenant boundaries · USD 37,604.40
- Google Firefly confused worker authority and storage boundaries
Google · Authorization and tenant boundaries · USD 60,000
- Google Application Integration mixed resource and service authority
Google · Authorization and tenant boundaries · USD 75,000
- Google support API exposed customer and agent data
Google · Authorization and tenant boundaries · USD 14,337
- Meta service-identity exposure amplified by excessive secret access
Meta · Cloud permissions and isolation · USD 150,000
- Meta Quest login migration lost OAuth credential confinement
Meta · Authentication and identity · USD 44,250
Sources
- Instagram account takeover via Meta Pixel script abuseYoussef Sammouda · reviewed 2026-10-02
- Facebook Bug Bounty and BountyCon US-dollar reportingDan Gurfinkel / Facebook · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot a066321c166a. Open the complete JSON contract.