vulns.co
/
GKData.io MCP and API Buy me a coffee

Vulnerability family

Memory safety and parser contracts

Safe length, lifetime, encoding, and component-boundary assumptions. 10 disclosures · 5 related references · 1 diagrams.

Disclosures

Related learning

Google Chrome for Developers Architecture Guide

Document Isolation Policy: process separation and residual authority

Chrome's Document Isolation Policy addresses information exposure within browser processes that origin checks alone cannot prevent. The guide explains how frames can be isolated independently while retaining popup…

Reviewed 2026-10-03

Chromium Project Architecture Guide

Chromium Rule of Two: input trust, memory safety and privilege

Chromium's Rule of Two says to avoid combining untrusted input, memory-unsafe code and high privilege in one component. The architecture policy covers safer parsing, separating privileges and reviewing unsafe code even…

Reviewed 2026-10-02

C++ Core Guidelines project Implementation Guide

C++ Core Guidelines: Bounds and Lifetime Safety

The C++ Core Guidelines connect three safety requirements: use objects with valid types, keep memory accesses within bounds, and ensure references do not outlive their objects. The bounds and lifetime sections explain…

Reviewed 2026-10-12

The Rust Project Implementation Guide

Rust Ownership and Borrowing: Lifetime Contracts

The Rust Book explains that each value has one owner, ownership can move, and the value is dropped when its owner leaves scope. Borrowing lets code access a value without taking ownership. References must remain valid,…

Reviewed 2026-10-12

The Rust Project Implementation Guide

Rust Slices: Bounds, Borrowing, and Text Boundaries

The Rust Book uses text processing to show why a borrowed slice stays tied to its source buffer while an integer position can become detached from the data it describes. The language reference explains that safe slice…

Reviewed 2026-10-12

Visual models

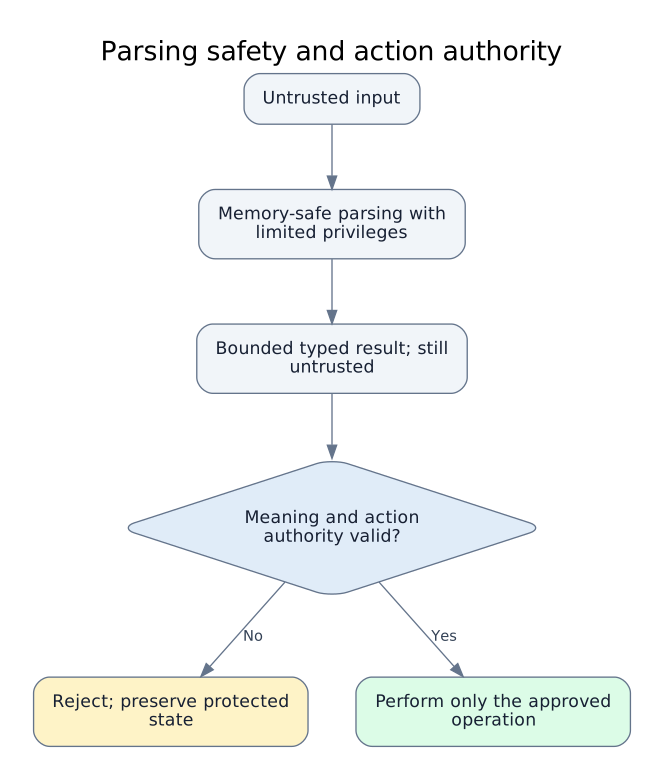
Untrusted input is parsed with memory safety and limited privileges. A bounded typed result still requires an independent meaning and authorization check before any scoped operation; failed checks reject the request.

Conceptual model Diagram

Parsing safety and action authority

Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.

Reviewed 2026-10-02

Related learning follows the topic crosswalk or an explicit diagram relationship. It does not classify a resource as a finding. Topics overlap, so their counts should not be added together.

Library synced 2026-11-18 · cases last reviewed 2026-10-05

af2809c308fc · JSON exports & schemas · CC BY 4.0 content / MIT software