Root cause
Lua garbage collection could leave an object referenced after its memory was freed, undermining the interpreter’s memory-safety assumptions.
Demonstrated impact
The vendor confirms possible native code execution by an authenticated user able to run Lua scripts. This crosses the scripting boundary; host impact remains dependent on process privileges and deployment isolation.
What to check for
- Review object-lifetime invariants across embedded interpreters and native components.
- Grant scripting access only where needed and retain least-privilege service execution.
- Check corrected vendor release guidance instead of relying on an early fixed-version summary.
Award and evidence
How the award was verified, and what the record does not establish
One competition-entry award, not the researchers’ event total. Official rules specify US currency; recipient allocation and actual cash settlement are unverified.
- Single competition-entry award; individual recipient splits and cash-transfer date are unknown.
- The October 6 article is the primary research publication; May demonstration and October 3 vendor advisory are distinct events.
- Vendor Redis Software release labels were corrected on October 27 and October 30, 2025; this record does not assume every product variant was fixed in its originally listed version.
Timeline
- Published
- 2025-10-06explicit · Primary research article publication; earlier competition results are separately dated.
- Public Disclosure
- 2025-05-16explicit · Public demonstration and result; vendor technical advisory followed later.
- Reported
- 2025-05-16explicit · Researcher timeline explicitly ties this CVE to its May 16 Pwn2Own report.
- Awarded
- 2025-05-16explicit · Award announced for the named individual entry.
- Fixed
- 2025-10-03explicit · Researcher article states that Redis released its advisory and patched version on this date. This is not a universal customer-deployment date; later vendor corrections affected some Redis Software fixed-version labels.
- Award Announced
- 2025-05-16explicit
Related visual models
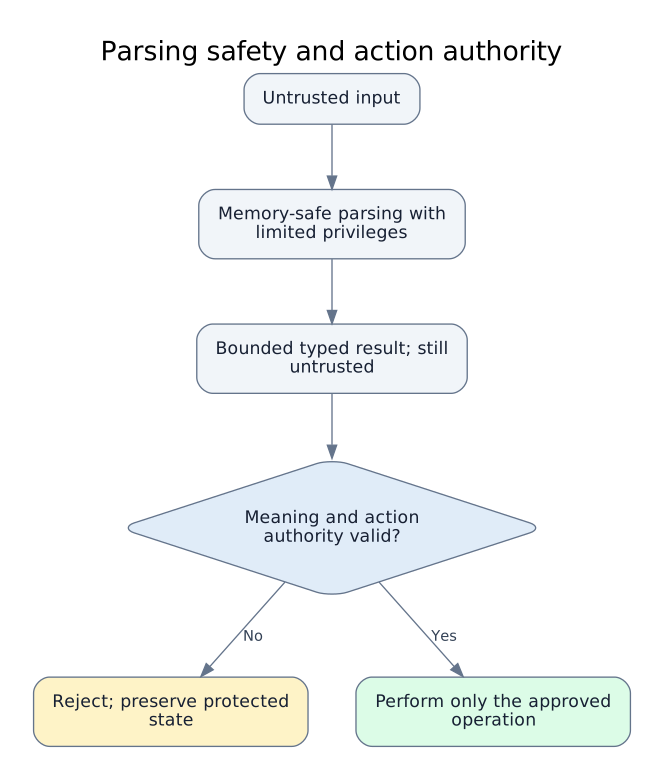
Parsing safety and action authority
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Related cases
- Redis replication state changes invalidated an active interpreter
Redis · Memory safety and parser contracts · USD 30,000
- Redis deserialization cleanup violated object-ownership invariants
Redis · Memory safety and parser contracts · USD 30,000
- PostgreSQL cryptographic parsing omitted a buffer-capacity check
PostgreSQL · Memory safety and parser contracts · USD 30,000
- PostgreSQL text-encoding invariant failure caused memory corruption
PostgreSQL · Memory safety and parser contracts · USD 30,000
Sources
- RediShell: Redis CVE-2025-49844Benny Isaacs and Nir Brakha / Wiz Research · reviewed 2026-10-02
- Pwn2Own Berlin 2025 daily resultsDustin Childs / Zero Day Initiative · reviewed 2026-10-02
- Pwn2Own Berlin 2025 rulesTrend Micro Zero Day Initiative · reviewed 2026-10-02
- Redis Lua Use-After-Free security advisoryRedis maintainers · reviewed 2026-10-02
- Redis CVE-2025-49844 remediation guidance and correctionsRiaz Lakhani / Redis · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.