vulns.co
/
GKData.io MCP and API Buy me a coffee

Security theme

Client and browser security

Client-side isolation, memory safety, and security-sensitive state. 20 disclosures · 4 related references · 3 diagrams.

Disclosures

Related learning

Chromium Project Architecture Guide

Chromium Rule of Two: input trust, memory safety and privilege

Chromium's Rule of Two says to avoid combining untrusted input, memory-unsafe code and high privilege in one component. The architecture policy covers safer parsing, separating privileges and reviewing unsafe code even…

Reviewed 2026-10-02

OWASP Cheat Sheet Series Implementation Guide

Authorization Cheat Sheet

OWASP recommends granting only needed permissions, denying access by default and making consistent authorization decisions on every request. The guidance also covers failure handling, logging and regression tests for…

Reviewed 2026-10-02

OWASP Cheat Sheet Series Implementation Guide

HTML5 Security Cheat Sheet: Web Messaging

OWASP explains how to check a browser message's origin and format and handle its contents as data. These are separate controls: verifying the sender does not replace validating the message or handling its content safely.

Reviewed 2026-10-02

OWASP Cheat Sheet Series Architecture Guide

LLM Prompt Injection Prevention Cheat Sheet

OWASP recommends layered defenses for LLM applications that read untrusted content or use tools. The guidance covers tracking data sources, limiting permissions, authorizing actions and monitoring behavior, while…

Reviewed 2026-10-02

Visual models

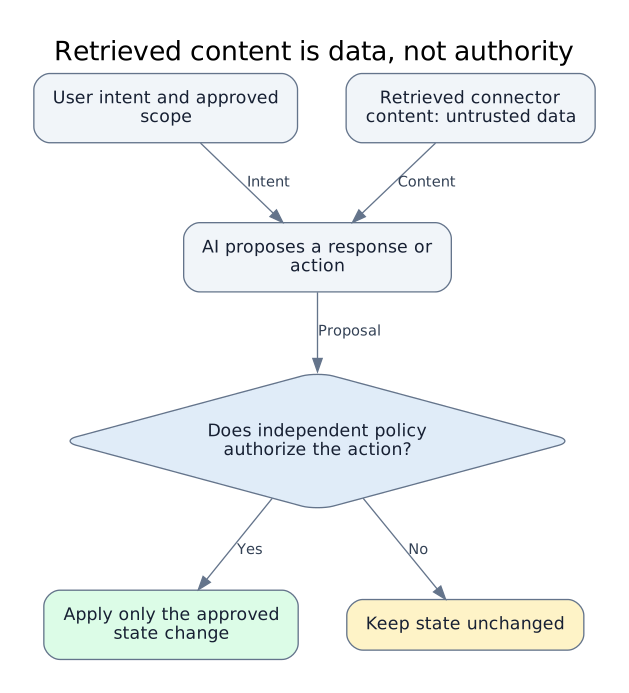
User intent and untrusted connector content enter the AI workflow separately. A proposed action reaches an independent policy decision. Only an authorized state change proceeds; otherwise state remains unchanged.

Conceptual model Diagram

Retrieved content is data, not authority

Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.

Reviewed 2026-10-02
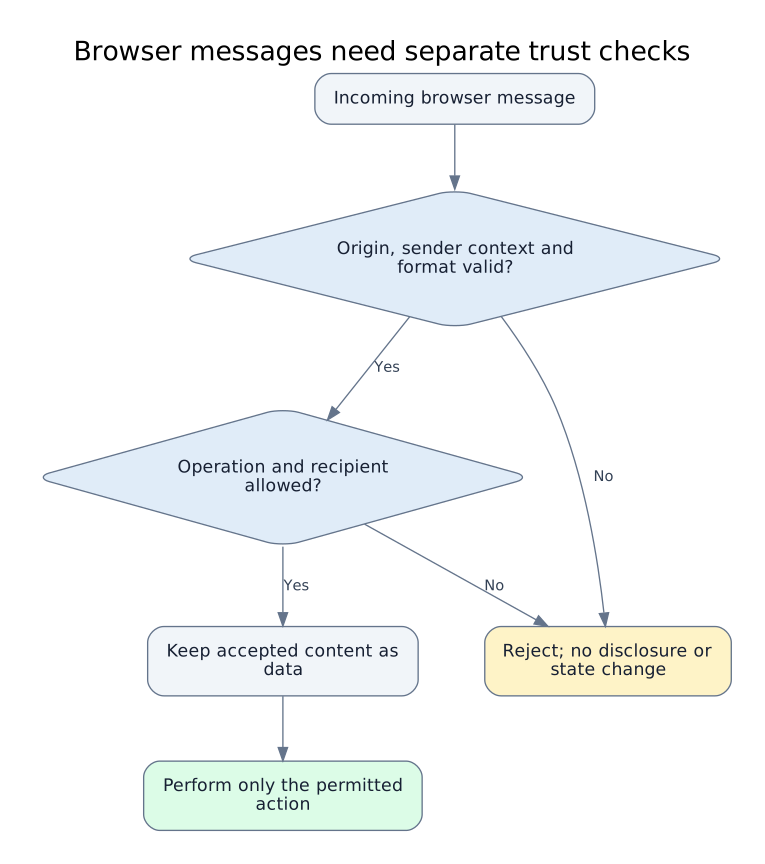
An incoming browser message first passes origin, sender-context and format validation. A separate decision checks the operation and recipient. Failed checks reject the message without disclosure or state change. Approved content remains data and only the permitted action is performed.

Conceptual model Diagram

Browser messages need separate trust checks

Original defensive model combining OWASP messaging and authorization guidance with the linked historical cases. These are independent design checks, not a vendor patch diagram or an operational reproduction.

Reviewed 2026-10-02
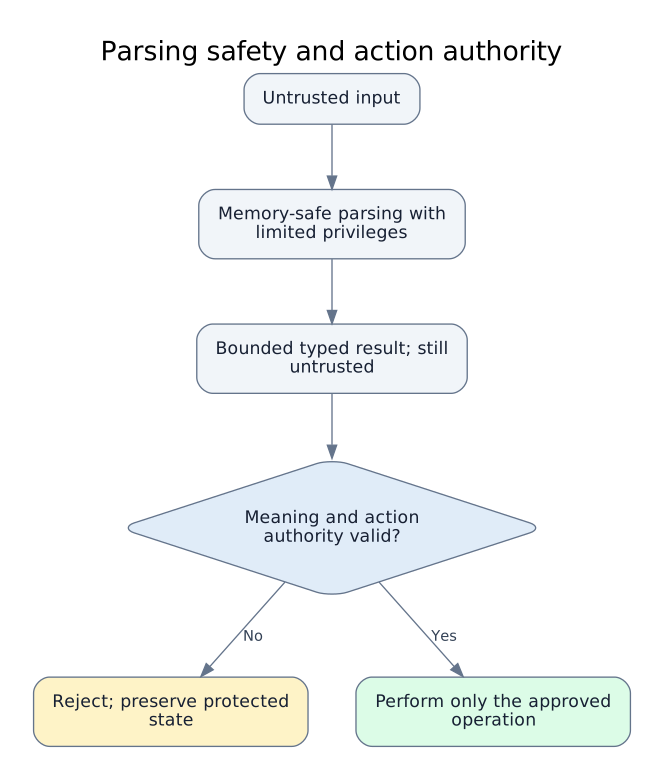
Untrusted input is parsed with memory safety and limited privileges. A bounded typed result still requires an independent meaning and authorization check before any scoped operation; failed checks reject the request.

Conceptual model Diagram

Parsing safety and action authority

Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.

Reviewed 2026-10-02

Related learning follows the topic crosswalk or an explicit diagram relationship. It does not classify a resource as a finding. Topics overlap, so their counts should not be added together.

Library synced 2026-11-18 · cases last reviewed 2026-10-05

af2809c308fc · JSON exports & schemas · CC BY 4.0 content / MIT software