How to use this reference
For an owned component, map input origin, language guarantees and execution privilege. Keep semantic authorization separate from successful parsing.
Before reading
- Basic understanding of parsing, process privileges and memory lifetime
Context and limits
- Memory safety does not establish data trust or permission to perform an operation.
- Chromium-specific exceptions are not blanket guarantees for other projects.
Related visual models
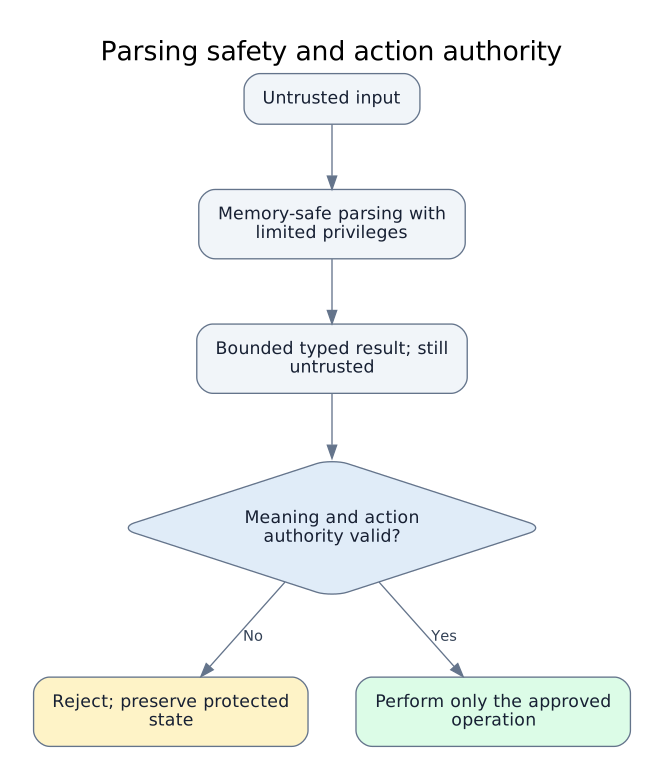
Parsing safety and action authority
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Reviewed 2026-10-02Read
Sources and provenance
- The Rule Of 2 Chromium Project · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot d5550c789111. Open the complete JSON contract.