vulns.co
/
GKData.io MCP and API Buy me a coffee

Vulnerability family

Business logic and concurrency

State transitions, approval integrity, and transactional invariants. 14 disclosures · 36 related references · 4 diagrams.

Disclosures

Related learning

Bugsink Maintainer Advisory

Bugsink: time-unit consistency in account-access token expiry

Bugsink interpreted token lifetimes expressed in seconds as days. Its maintainer reports that unused email-verification, password-reset and new-user setup links therefore stayed valid beyond their intended expiry.

Reviewed 2026-10-03

Directus Maintainer Advisory

Directus: denied mutations must leave dependent state unchanged

Directus could reject a change after cleanup had already modified application state. Its maintainer advisory describes disconnected automation links, removed attribution metadata and invalidated permission caches…

Reviewed 2026-10-03

File Browser Maintainer Advisory

File Browser: existing shares must follow current owner permissions

File Browser's maintainer reports that existing public share links still allowed downloads after the owner's permissions were revoked in version 2.62.2. Creating the share required both sharing and download permissions,…

Reviewed 2026-10-03

Google Implementation Guide

Google API field masks: preserve server-owned and immutable state

Google's approved field-mask guidance defines which fields an update selects, while separate field rules determine what may change. Services must ignore output-only input even when a containing field is selected; the…

Reviewed 2026-10-04

HotCRP Maintainer Advisory

HotCRP: separate submission visibility from authorship authority

HotCRP allowed permission to view a submission to extend to changing its contact authorship. The maintainer reports that reviewers and program-committee members could gain author-level access to submissions they could…

Reviewed 2026-10-03

MythicalDash Maintainer Advisory

MythicalDash: payment evidence must establish credit entitlement

MythicalDash could grant spendable account credit from a pending payment before the provider confirmed settlement. Its maintainer advisory reports unpaid credits in a controlled deployment. The balance update was…

Reviewed 2026-10-04

n8n Maintainer Advisory

n8n: directory-attribute authority in durable account linking

n8n's maintainer advisory describes account linking that treated a matching LDAP email attribute as proof of account ownership (CVE-2026-33665). It reports that access to the linked account, including administrator…

Reviewed 2026-10-03

OpenFGA Maintainer Advisory

OpenFGA: policy intersections must preserve explicit exclusions

OpenFGA's maintainer advisory describes excluded users incorrectly returning in user-enumeration results (CVE-2026-61709). This happened with a particular combination of wildcard membership, exclusion and intersection,…

Reviewed 2026-10-03

Outline Maintainer Advisory

Outline: integration authority must end with its owning account

Outline's maintainer-published report demonstrates document content still being delivered by a webhook after its administrator creator's account was deleted (GHSA-33jq-x32c-3ccw). Account cleanup left the subscription…

Reviewed 2026-10-03

OWASP Cheat Sheet Series Implementation Guide

OWASP Forgot Password

OWASP explains how to bind recovery challenges to the right account, limit their lifetime and reuse, and control repeated attempts. It also covers consistent responses, user notifications and session handling after a…

Reviewed 2026-10-07

OWASP Cheat Sheet Series Implementation Guide

Authorization Cheat Sheet

OWASP recommends granting only needed permissions, denying access by default and making consistent authorization decisions on every request. The guidance also covers failure handling, logging and regression tests for…

Reviewed 2026-10-02

OWASP Cheat Sheet Series Implementation Guide

OWASP Secure Code Review: baseline and change-focused review

OWASP explains the different purposes of a whole-codebase review and a review focused on changes. It connects architecture, business rules and existing findings to examination of data flow, security checks and workflow…

Reviewed 2026-10-03

OWASP Cheat Sheet Series Architecture Guide

OWASP Threat Modeling: system assumptions and mitigation validation

OWASP describes a repeated design-review process that connects a model of the system to possible threats, agreed responses and validation. Data-flow diagrams and structured questions help reveal dependencies and missing…

Reviewed 2026-10-03

OWASP Cheat Sheet Series Implementation Guide

OWASP Transaction Authorization

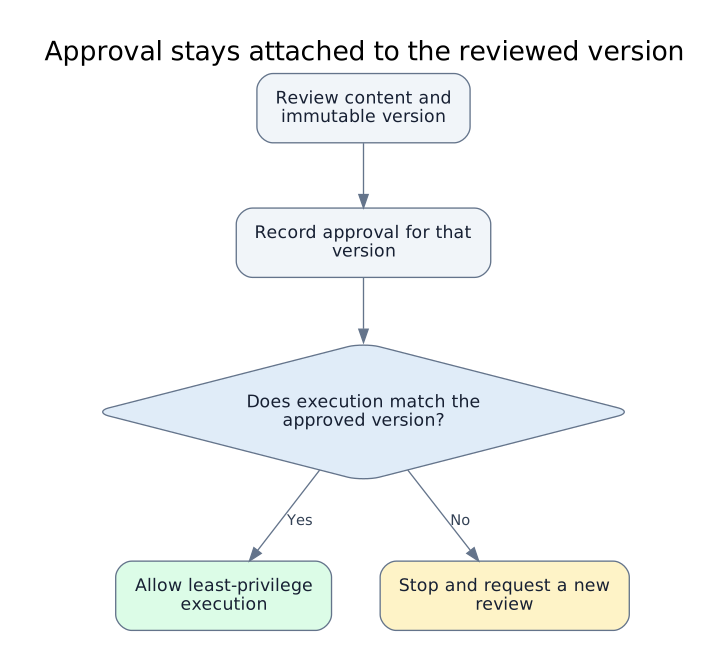
OWASP explains how to tie approval to a specific operation and its important details. Applications must preserve the approved data, enforce valid workflow steps and check authorization again when the operation runs.

Reviewed 2026-10-02

PortSwigger Training Lab

Web Security Academy: Free Online Training from PortSwigger

PortSwigger offers free web-security lessons and purpose-built interactive training environments. Topics include authentication, access control, business logic, API security and other application-security fundamentals.

Reviewed 2026-10-02

PostgreSQL Global Development Group Implementation Guide

PostgreSQL 18: Transaction Isolation and Business Invariants

PostgreSQL explains why a stable database snapshot does not, by itself, preserve business rules when transactions overlap. Its guidance distinguishes serializable consistency from explicit locking. Retrying after a…

Reviewed 2026-10-03

Internet Engineering Task Force / RFC Editor Technical Standard

RFC 9700: Best Current Practice for OAuth 2.0 Security

RFC 9700 updates OAuth security guidance using deployment experience and stronger protocol requirements. It identifies insecure patterns to stop using and provides a primary reference for reviewing identity integrations.

Reviewed 2026-10-06

Saleor maintainers Maintainer Advisory

Saleor email changes: bind confirmation to account and state

Saleor did not check that an email-change confirmation token belonged to the signed-in account. The maintainer's scenario requires a valid token for one account and authenticated access to another; it describes possible…

Reviewed 2026-10-06

Spree Maintainer Advisory

Spree: cart association must retain guest-possession checks

Spree let a signed-in customer claim an unowned guest cart without checking proof that the cart was theirs. The maintainer describes recoverable ownership and email changes, plus disclosure of checkout addresses if the…

Reviewed 2026-10-03

Stripe Implementation Guide

Stripe webhooks: authentic delivery and business-state integrity

A valid Stripe webhook signature proves delivery authenticity, not that an event is new or reflects the latest business state. Stripe's guidance explains that events can arrive more than once or out of order, and…

Reviewed 2026-10-03

Vikunja Maintainer Advisory

Vikunja: saved favorites must recheck current project access

Vikunja could keep showing favorited tasks after project access was revoked because search did not recheck current permissions. The maintainer reports that updated titles and descriptions remained readable, despite…

Reviewed 2026-10-03

Visual models

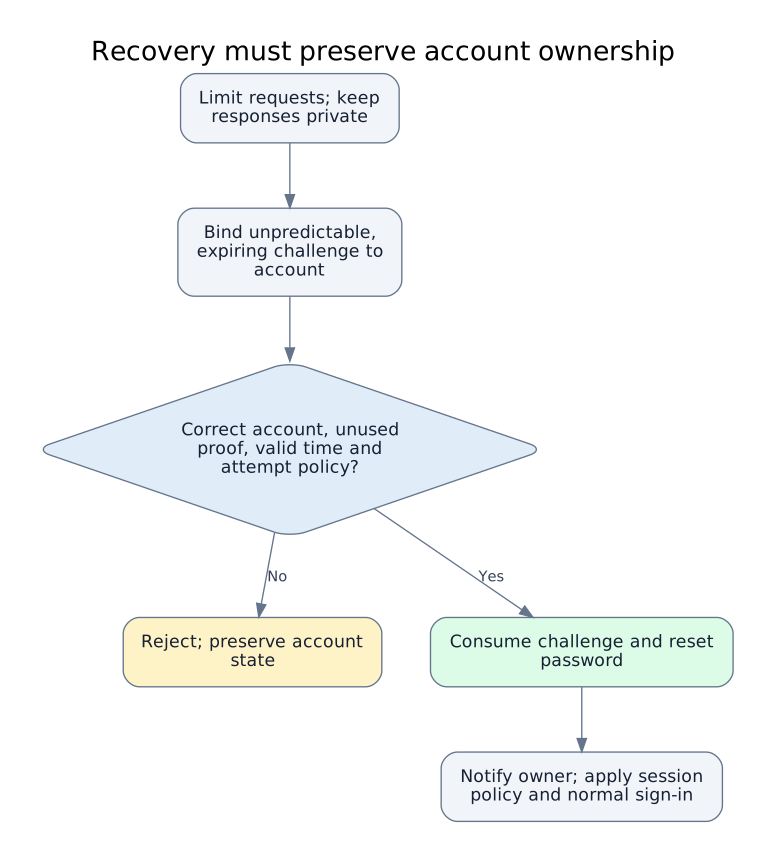
A limited recovery request creates an account-bound challenge. Only valid, unexpired, unused proof permits a reset. Failure preserves account state; success consumes the challenge and notifies the owner.

Conceptual model Diagram

Recovery must preserve account ownership

Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.

Reviewed 2026-10-02
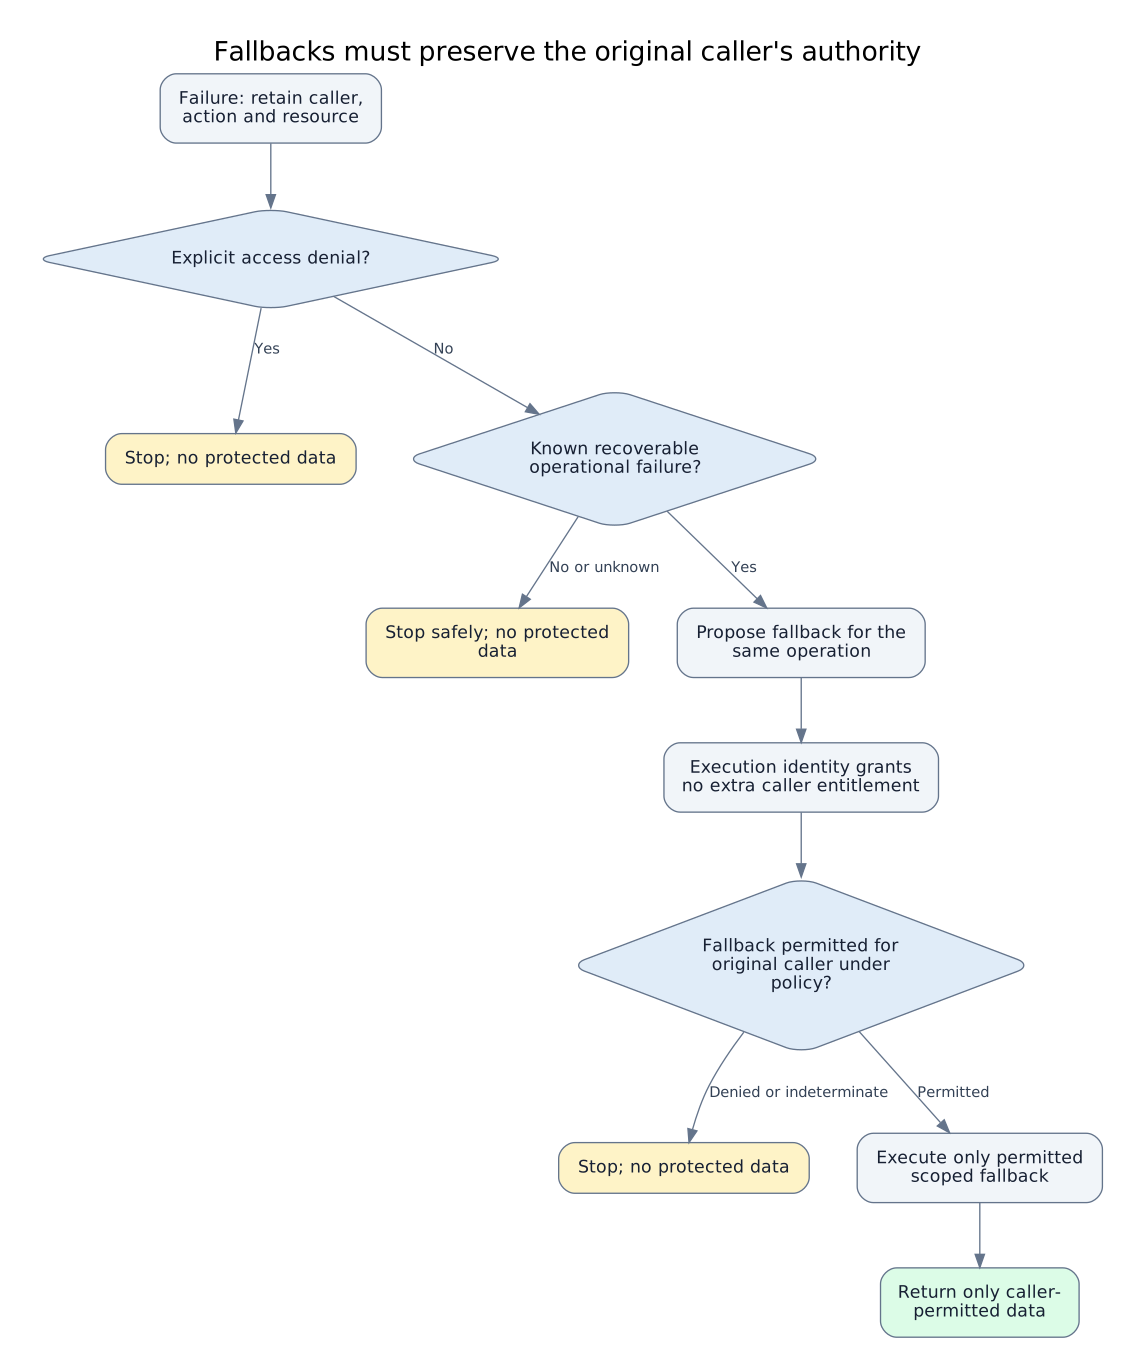
A failure retains the original caller, action and resource. An explicit access denial stops without protected data. A known recoverable operational failure can propose a fallback, but switching execution identity grants no extra caller entitlement. A separate application-policy decision evaluates that fallback for the original caller. Denied or indeterminate decisions stop without protected data. A permitted, scoped fallback returns only caller-permitted data.

Conceptual model Diagram

Fallbacks must preserve the original caller's authority

Original editorial defensive synthesis of the Instagram embedding disclosure and OWASP authorization guidance. The researcher attributes the disclosure to error handling that retrieved protected content under an…

Reviewed 2026-10-04
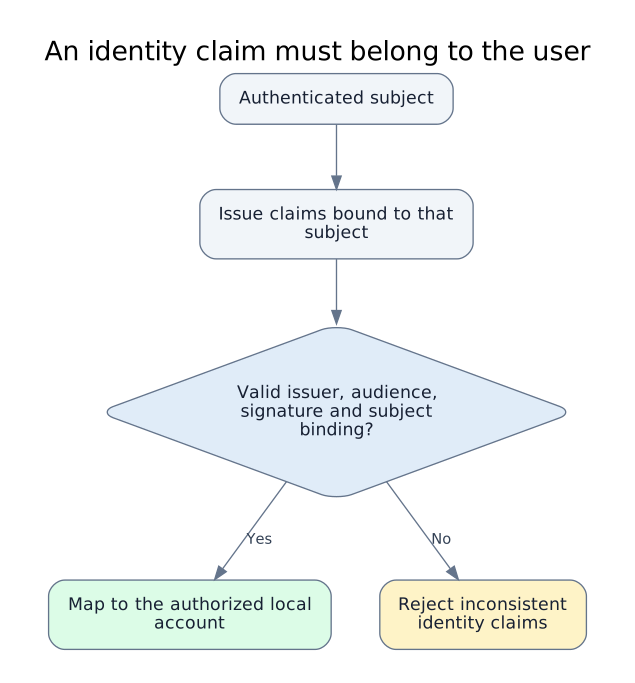
The identity provider authenticates a subject and binds issued claims to it. The relying application validates the issuer, audience, signature, and ownership binding before mapping to a local account. Failed validation is rejected.

Conceptual model Diagram

An identity claim must belong to the user

Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.

Reviewed 2026-10-02

Related learning follows the topic crosswalk or an explicit diagram relationship. It does not classify a resource as a finding. Topics overlap, so their counts should not be added together.

Library synced 2026-11-18 · cases last reviewed 2026-10-05

af2809c308fc · JSON exports & schemas · CC BY 4.0 content / MIT software