How to use this reference
The stated repair retains the granted resource in refresh-token state and rejects conflicting resource choices. The maintainer also calls for renewed authorization after upgrading because older refresh tokens lack this binding; temporary restrictions are incomplete mitigation. Editorial lesson: review authorization invariants throughout a grant’s lifecycle, including migration of pre-fix state.
Before reading
- OAuth grant, refresh, resource, and consent concepts
- Distinguishing a user’s permissions from the smaller authority delegated to a client
Context and limits
- CVE-2026-86073. The advisory credits bariskececi as reporter; Matsuuu is its publishing maintainer.
- Prerequisites include client registration, authenticated user consent for one protected workflow, and another identifiable workflow within that user’s execution permissions.
- The patched-version table lists 2.38.2 and 2.37.7, while prose says 2.38.1 and 2.37.7. No corrected affected interval is inferred.
- Official release pages date both 2.38.2 and 2.37.7 to September 2, 2026, separately from September 3 advisory publication; 2.38.2 is labeled pre-release. Release existence does not resolve the advisory inconsistency.
- No bounty is established. Learning prerequisites and general design guidance are editorial.
Related visual models
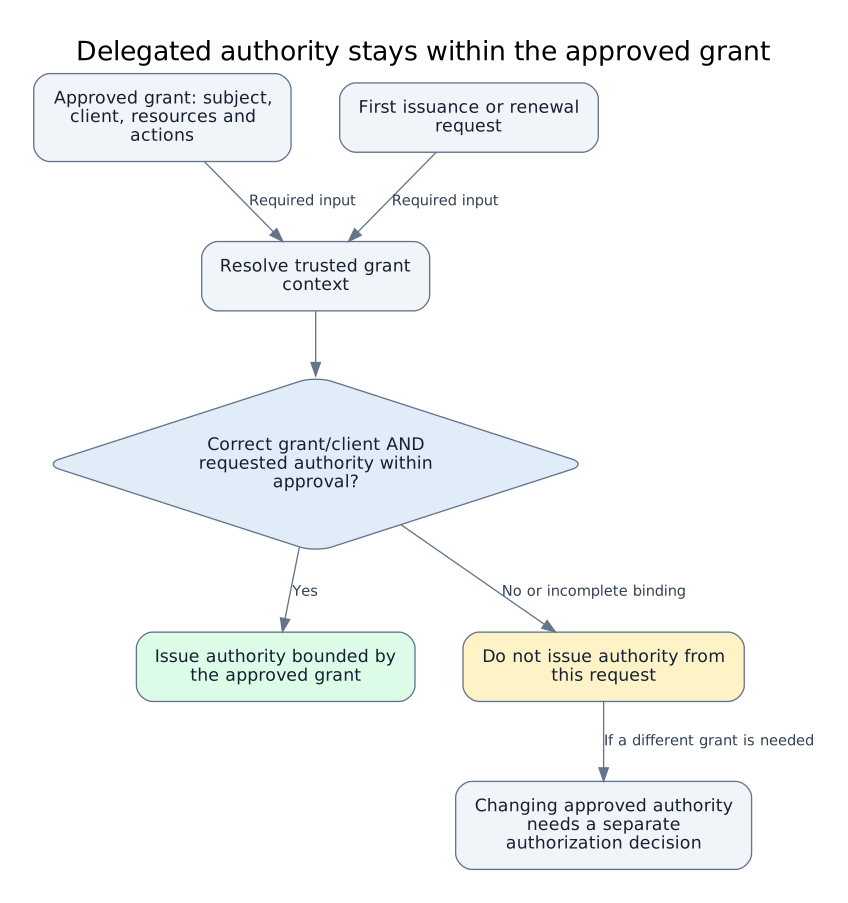
Delegated authority stays within the approved grant
Original editorial defensive synthesis, not a vendor architecture, protocol sequence or independently verified patch. The Google researcher describes lost client and permission binding through a device grant; proposed…
Reviewed 2026-10-04Read
Sources and provenance
- Per-Resource OAuth Consent Bypass via Unbound Refresh Token Resource Substitution n8n · reviewed 2026-10-03
- n8n@2.38.2 release n8n · reviewed 2026-10-03
- n8n@2.37.7 release n8n · reviewed 2026-10-03
Record reviewed 2026-10-03. Snapshot d5550c789111. Open the complete JSON contract.