The conceptual model
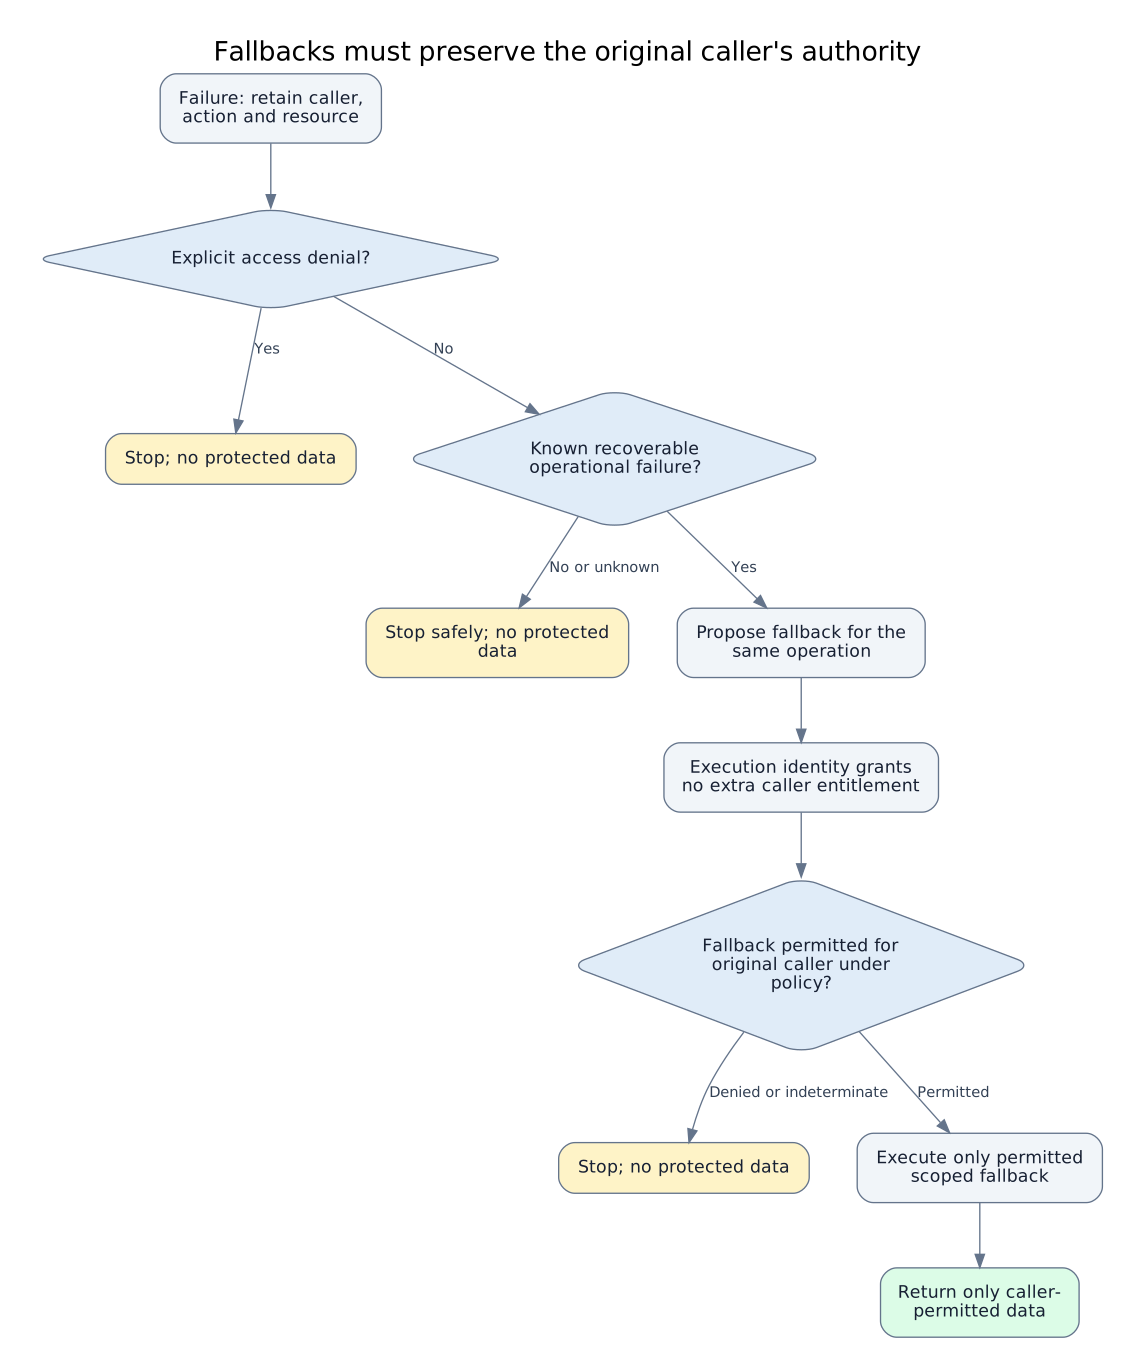
Cases and references behind the model
Sources and provenance
- 003random.com Primary source
- cheatsheetseries.owasp.org Primary source
Record reviewed 2026-10-04. Snapshot d5550c789111. Open the complete JSON contract.
Conceptual model · 1 min read
Original editorial defensive synthesis of the Instagram embedding disclosure and OWASP authorization guidance. The researcher attributes the disclosure to error handling that retrieved protected content under an elevated service identity, relaying vendor clarification rather than independently published vendor evidence. OWASP supports consistent per-request permissions and safe handling of failed authorization checks. The graph models a safe recovery decision, not Instagram's architecture or a documented patch. An explicit access denial terminates this logical operation; only a known recoverable operational failure may reach fallback review. The original caller, action and resource remain the policy context, even if execution identity changes. Denied or indeterminate fallback authorization stops without protected data. Assumes the same caller and logical operation with an application-defined recovery policy; separately authorized service or background work is excluded. Permission freshness, revocation, distributed consistency and diagnostic minimization are outside this model.
Record reviewed 2026-10-04. Snapshot d5550c789111. Open the complete JSON contract.
GitHub snapshot 2026-10-04
d5550c789111 · JSON exports & schemas · CC BY 4.0 content / MIT software
| / | Focus search on this page |
| Ctrl K | Search everything (command palette) |
| 1-9 | Library, Generator, Playbooks, Gadgets, Checklists, Payloads, Bypasses, Utilities, Reports |
| 0 | AI / MCP connector |
| j / k | Move selection down / up |
| Enter | Expand / open selected |
| c | Copy primary command of selected |
| f | Toggle favorite on selected tool |
| Esc | Clear search / close |