Root cause
Recovery controls did not enforce attempt limits consistently across simultaneous verification operations. Defensive reviews should verify atomic, account-bound limits and consistent treatment of recovery and multifactor checks.
Demonstrated impact
Potential account takeover; the researcher says Microsoft classified severity as Important because practical exploitation required substantial resources.
What to check for
- Bind recovery attempts and verification state to the intended account.
- Use atomic security counters and test concurrent state transitions locally.
Award and evidence
How the award was verified, and what the record does not establish
Researcher says the bounty was received on February 9, 2021; that is the payment date, not a separately confirmed award-decision date.
- The article header now shows a 2024 update; its archive preserves March 2, 2021 publication
- No independent vendor-hosted payout confirmation retrieved
- Current article update: 2024-12-06; original publication is stored separately.
Timeline
- Published
- 2021-03-02explicit · Original publication date preserved by the author’s archive; current article header is a later update.
- Fixed
- 2020-11explicit
- Paid
- 2021-02-09explicit
Related visual models
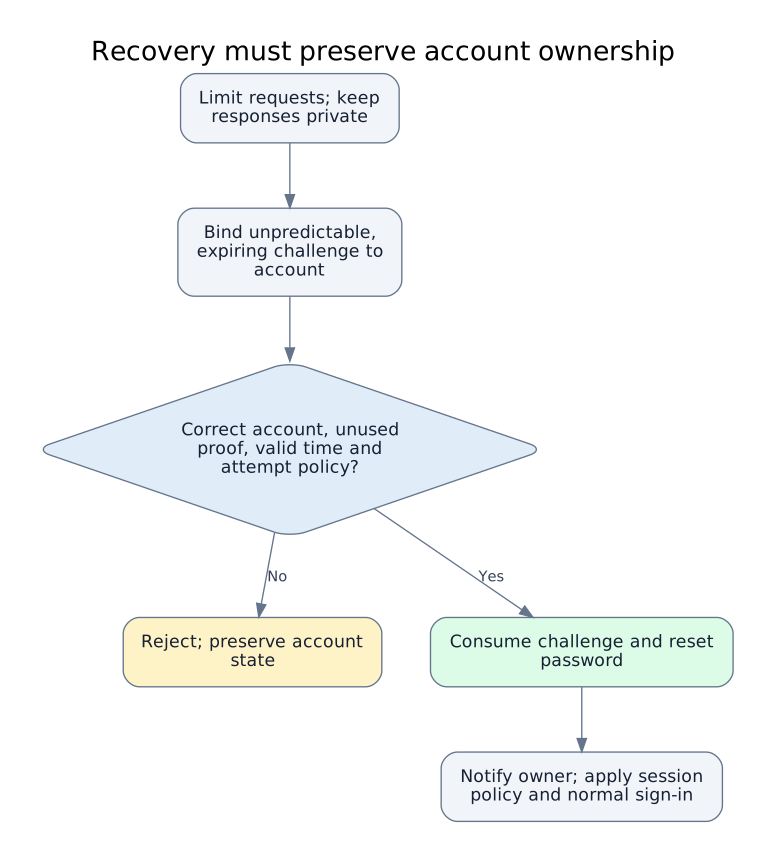
Recovery must preserve account ownership
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Related cases
- Google device grants lost client and permission binding
Google · Authentication and identity · USD 13,337
- GitLab recovery delivery lacked verified-address binding
GitLab · Authentication and identity · USD 35,000
- LiteSpeed Cache privileged user simulation relied on weak security tokens
LiteSpeed Technologies · Authentication and identity · USD 14,400
- Meta Quest login migration lost OAuth credential confinement
Meta · Authentication and identity · USD 44,250
- Kestrel HTTP framing differed across proxy and application boundaries
Microsoft · Injection and untrusted input · USD 10,000
Sources
- Microsoft account recovery lacked consistent attempt-limit enforcementLaxman Muthiyah · reviewed 2026-10-02
- Original publication archiveLaxman Muthiyah · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.