Root cause
V8 sped up property lookups by caching assumptions about the objects that supplied them. For prototype chains involving WebAssembly objects, changes to an object's structure did not always invalidate those assumptions. An optimized handler could then use the wrong type assumptions.
Demonstrated impact
Memory read/write was possible. The researcher describes possible code execution within Chrome's renderer when combined with a separate V8 heap-sandbox escape. This does not establish escape from the renderer's process sandbox or full-machine compromise.
What to check for
- Optimized execution must invalidate cached assumptions when object state changes and handle all supported object families consistently.
- Distinguish issue-status fixes from stable-release availability.
Award and evidence
How the award was verified, and what the record does not establish
Case notices use $; USD is contextual from the official Chromium program source. No currency conversion or cash-receipt claim.
- Case notices use dollar notation; USD denomination relies on official Chromium program context.
- Award decisions are established; payment completion is not.
- Fixed status and publicly available stable release are separate dates.
- Release list revised November 17, 2025; it identifies the newly added entries separately as CVE-2025-13226 through 13230. This record retains the October 28 release disclosure.
Timeline
- Published
- 2026-03-17explicit · Detailed researcher advisory; public issue access opened January 13, 2026, after the October 2025 vendor notice.
- Public Disclosure
- 2025-10-28explicit · Vendor release disclosure; full issue access was enabled later.
- Reported
- 2025-09-26explicit
- Awarded
- 2025-10-14explicit
- Fixed
- 2025-10-28explicit · Documented stable release; issue was marked Fixed 2025-10-06. Backport availability may differ.
- Award Announced
- 2025-10-28explicit · Per-issue reward listed in the public release notice.
Related visual models
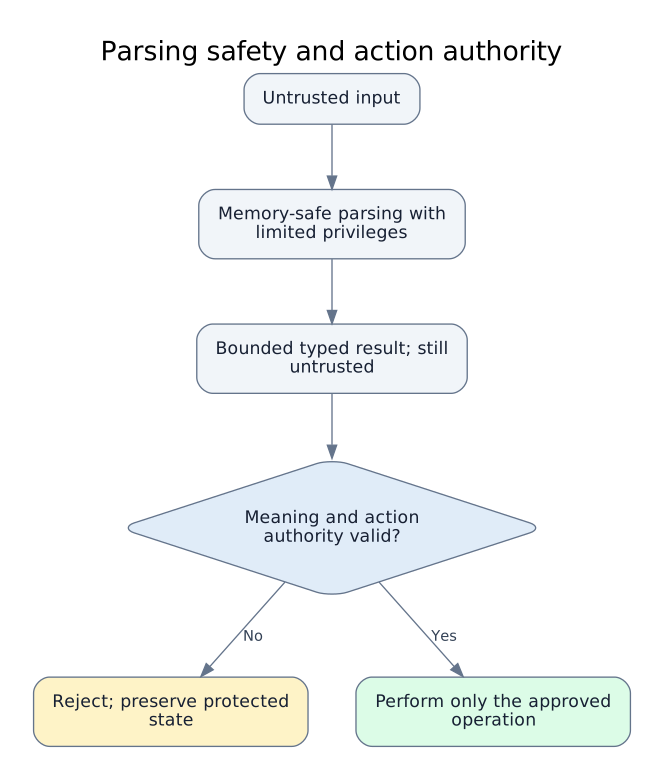
Parsing safety and action authority
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Related cases
- Redis replication state changes invalidated an active interpreter
Redis · Memory safety and parser contracts · USD 30,000
- Redis deserialization cleanup violated object-ownership invariants
Redis · Memory safety and parser contracts · USD 30,000
- PostgreSQL cryptographic parsing omitted a buffer-capacity check
PostgreSQL · Memory safety and parser contracts · USD 30,000
- PostgreSQL text-encoding invariant failure caused memory corruption
PostgreSQL · Memory safety and parser contracts · USD 30,000
- Google Mamba temporary outputs lacked access isolation
Google · Authorization and tenant boundaries · USD 37,604.40
- Google Firefly confused worker authority and storage boundaries
Google · Authorization and tenant boundaries · USD 60,000
Sources
- Chromium issue 447613211Google Chromium security team · reviewed 2026-10-02
- Chrome Stable Channel Update for Desktop, 2025-10-28Google Chrome team · reviewed 2026-10-02
- Security rewards at Google: Two MEEELLION Dollars LaterChromium team · reviewed 2026-10-02
- GHSL-2025-114: Chromium V8 advisoryMan Yue Mo / GitHub Security Lab · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.