Root cause
Content considered inert by Gemini could acquire active rendering behavior in Colab. The integration did not preserve the same sanitization contract across that boundary.
Demonstrated impact
The researcher reports confirming Workspace-data disclosure after a user exported content to Colab. The scenario depended on Gemini encountering untrusted content and having access to connected data. Suggested delivery through poisoned training data or embeddings was not separately demonstrated.
What to check for
- Maintain consistent content-handling contracts across integration boundaries.
- Enforce output destinations independently from generated or retrieved text.
- Treat export as a new interpretation boundary; validate the destination representation rather than assuming upstream sanitization remains effective.
Award and evidence
How the award was verified, and what the record does not establish
This amount belongs to the Colab finding; a separate Gemini-only finding was marked duplicate.
- Award correspondence is researcher-published; settlement is not independently verified.
- The separate Gemini-only finding was a duplicate, not another award.
- No exact publication day, fix date or vendor patch design is established.
Timeline
- Published
- 2025-11explicit · Author homepage supplies November 2025; exact publication day is not established.
- Reported
- 2025-04-30explicit
- Awarded
- 2025-05-20explicit
Related visual models
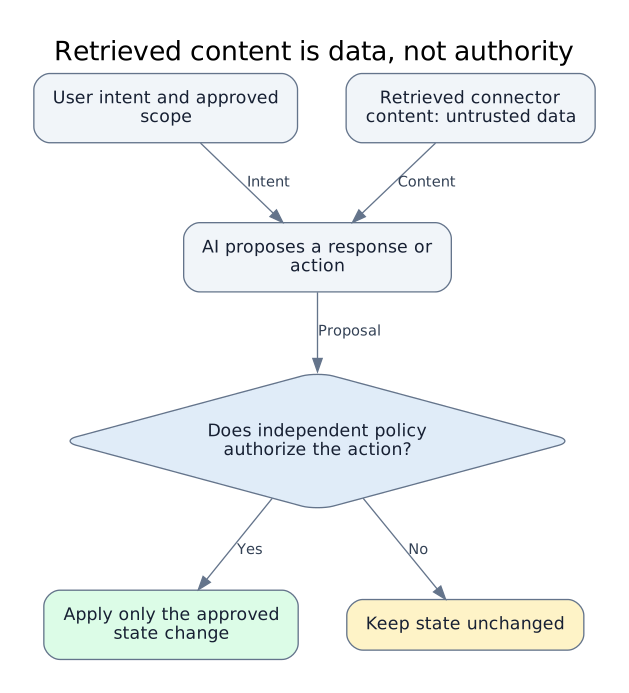
Retrieved content is data, not authority
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Related cases
- Codex metadata collection trusted repository execution helpers
OpenAI · AI integration boundaries · USD 10,000
- Codex automated Git operations trusted repository hook settings
OpenAI · AI integration boundaries · USD 20,000
- Gemini Enterprise connected-content trust failure allowed persistent-memory modification
Google · AI integration boundaries · USD 15,000
- Bard Workspace integration weakened output-data boundaries
Google · AI integration boundaries · USD 20,000
- Google Mamba temporary outputs lacked access isolation
Google · Authorization and tenant boundaries · USD 37,604.40
- Google Firefly confused worker authority and storage boundaries
Google · Authorization and tenant boundaries · USD 60,000
Sources
- Hacking Gemini: A Multi-Layered ApproachValentino Massaro · reviewed 2026-10-03
- Valentino’s issue trackerValentino Massaro · reviewed 2026-10-03
Record reviewed 2026-10-03. Snapshot af2809c308fc. Open the complete JSON contract.