How to use this reference
Document the expected sender, operation, recipient and permitted data for browser messages. Review identity checks, data validation, application authorization and rendering safety separately in owned application designs.
Before reading
- Basic browser origin and document concepts
- Familiarity with event-driven JavaScript
Context and limits
- Living guidance; review supported browser behavior and application context before implementation.
- Origin and format validation do not by themselves define which business operations or disclosures are authorized.
Related visual models
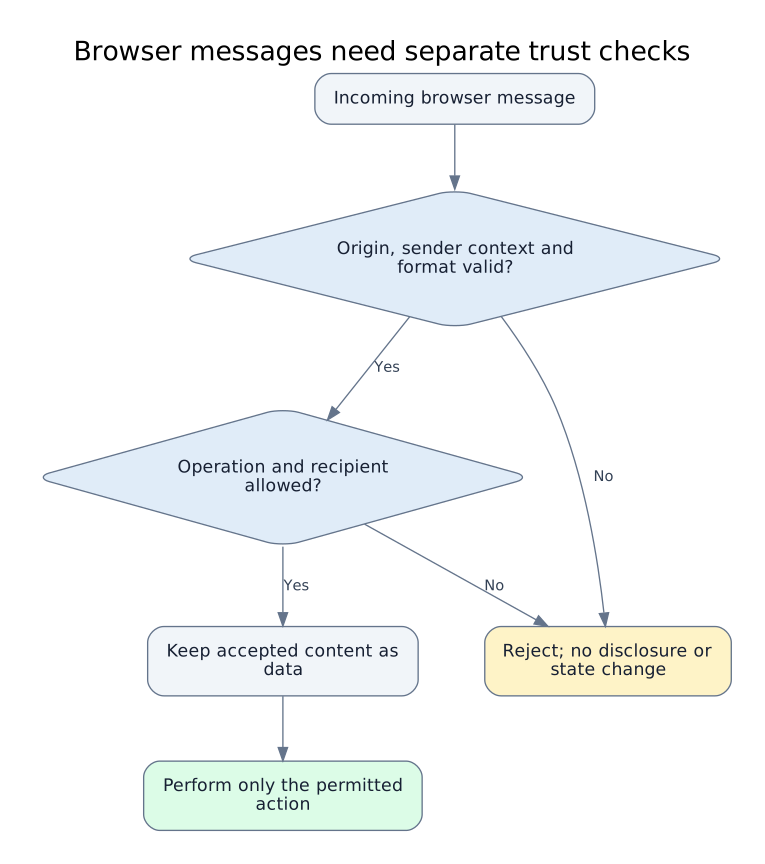
Browser messages need separate trust checks
Original defensive model combining OWASP messaging and authorization guidance with the linked historical cases. These are independent design checks, not a vendor patch diagram or an operational reproduction.
Reviewed 2026-10-02
Sources
- HTML5 Security Cheat Sheet: Web MessagingOWASP Cheat Sheet Series · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.