Root cause
The SDK treated a callback identifier as an authentication secret even though it came from non-cryptographic randomness. The researcher traced messages from an embedded plugin into the SDK’s handlers and checked how they were authorized. A separate handler rendered supplied content as active HTML. Checking the message’s origin alone did not prove that its content was authorized or safe to render.
Demonstrated impact
The researcher reports script execution and Facebook account takeover under mobile in-app browser conditions. Impact on an arbitrary embedding site depended on its framing controls. The article does not establish that every website using the SDK was affected equally.
What to check for
- Use cryptographic randomness and context binding for values that authorize message handling.
- Validate the sender, expected message relationship and permitted operation independently of rendering safety.
- Keep externally supplied content inert and review embedded-browser permissions as a separate trust boundary.
- Treat these as defensive design recommendations; the source dates a fix but does not establish the precise vendor patch implementation.
Award and evidence
How the award was verified, and what the record does not establish
One researcher-reported bug bounty, not an event total. The article uses $; prior official Meta program reporting supplies USD context. Actual cash settlement is not established.
- Researcher-reported award; no independent vendor confirmation or audited transfer.
- January 2026 page dates may reflect publication or archive migration; original disclosure is not established.
- USD normalization uses earlier official program context rather than an award receipt.
Timeline
- Reported
- 2023-06-22explicit
- Awarded
- 2023-06-28explicit
- Fixed
- 2023-12-15explicit · Researcher timeline explicitly labels this as the vendor fix date.
Related visual models
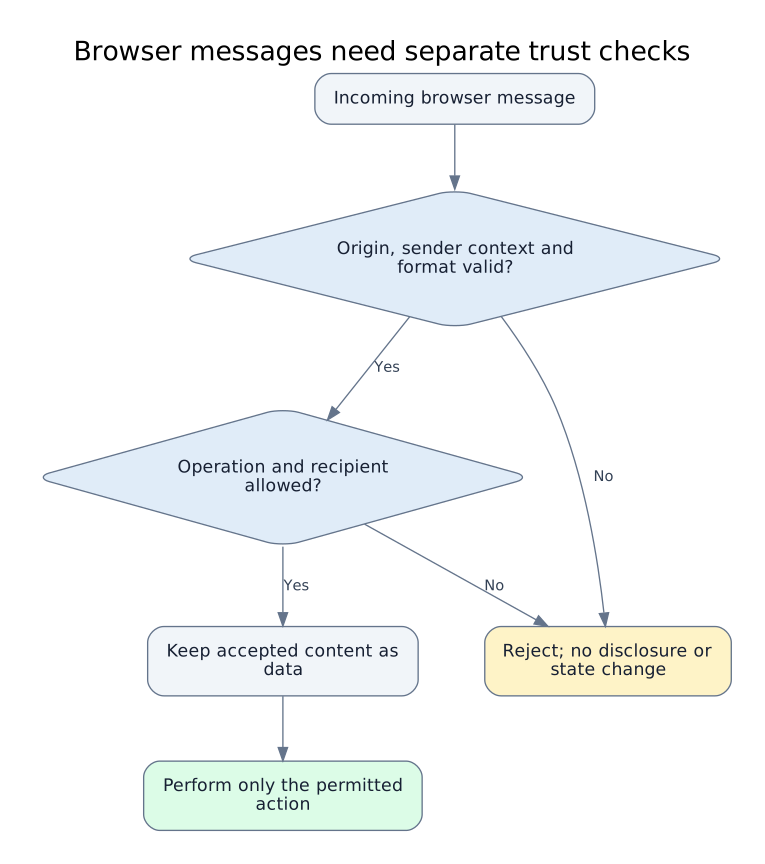
Browser messages need separate trust checks
Original defensive model combining OWASP messaging and authorization guidance with the linked historical cases. These are independent design checks, not a vendor patch diagram or an operational reproduction.
Related cases
- Google device grants lost client and permission binding
Google · Authentication and identity · USD 13,337
- GitLab recovery delivery lacked verified-address binding
GitLab · Authentication and identity · USD 35,000
- LiteSpeed Cache privileged user simulation relied on weak security tokens
LiteSpeed Technologies · Authentication and identity · USD 14,400
- Meta Quest login migration lost OAuth credential confinement
Meta · Authentication and identity · USD 44,250
- Meta service-identity exposure amplified by excessive secret access
Meta · Cloud permissions and isolation · USD 150,000
- Instagram embedding fallback changed the authorization context
Meta · Authorization and tenant boundaries · USD 14,500
Sources
- Account Takeover in Facebook mobile app due to usage of cryptographically unsecure random number generator and XSS in Facebook JS SDKYoussef Sammouda · reviewed 2026-10-02
- Facebook Bug Bounty and BountyCon US-dollar reportingDan Gurfinkel / Facebook · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.