Root cause
An internal user object and its sanitized public version used the same field name with different Ruby key types. According to the vendor, earlier serialization kept only the public version, but the framework upgrade emitted both. Snapshot tests parsed the response again and discarded the earlier duplicate, hiding private data that was still present in the raw output. This affected disclosed reports with a reporter or team-member summary. The failure concerned application output after a framework change, not an AI agent.
Demonstrated impact
The vendor reproduced private-attribute exposure. The public report describes personal and security-sensitive account attributes, but does not demonstrate account takeover or establish an affected-user count or wider exploitation. The vendor announced a deployed fix on February 21, 2025; the researcher retested and observed only intended public attributes for team and reporter summaries. The exact code change is not disclosed.
What to check for
- Construct public responses from explicit safe fields rather than relying on later serialization to overwrite an internal object.
- Test both raw serialized output and parsed structure; normalization can hide duplicate fields and sensitive data.
- Treat framework upgrades as changes to security-relevant output semantics, and exercise nested representations with private-field exclusion assertions.
Award and evidence
How the award was verified, and what the record does not establish
Vendor confirms the individual report’s reward; the public report records the award event on February 21, 2025, while settlement remains unreported. The award article uses a dollar sign; current official HackerOne standards supply USD context only. Exhibit C reproduces guideline version 1.2 dated July 29, 2019 and specifies USD on printed page 12, supplying historical platform context rather than individual payment proof.
- Award evidence does not establish settlement; the USD 25,000 amount comes from the case study, while the report hides the bounty amount.
- The technical report names the earlier Rails version as 6.1.7.9; the later case study says 6.1.7.10. Both identify the upgrade to 7.1.5.1; the discrepancy is unresolved.
- The case study describes retest validation within an hour, but visible retest-request and completion timestamps are about 72 minutes apart. Edited timeline timestamps and deployment timing limit precise duration comparisons.
- The public sources do not establish exact authentication prerequisites, affected-user count, a code-level patch, or successful account compromise.
- Currency context includes currently reviewed standards dated July 27, 2026 and historical platform guidelines; neither independently proves individual settlement.
Timeline
- Published
- 2025-04-01explicit · Public technical report disclosure date; the later vendor case study was published June 24, 2025.
- Public Disclosure
- 2025-04-01explicit
- Reported
- 2025-02-19explicit
- Awarded
- 2025-02-21explicit · Public timeline records the bounty event; the vendor case study establishes its USD 25,000 amount. Separate retest compensation is not included.
- Fixed
- 2025-02-21explicit · Vendor deployment confirmation and successful researcher retest appear on this day; exact deployment time is not established.
Related visual models
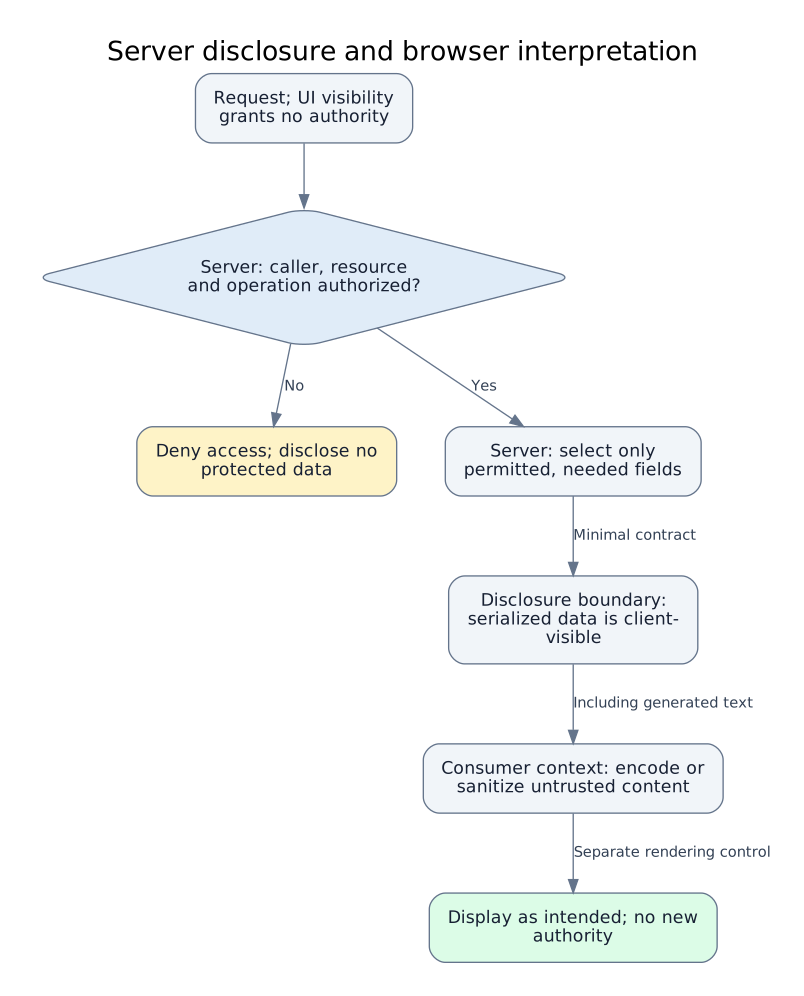
Server disclosure and browser interpretation
Editorial conceptual model: assumes an application with server-side privileged data and a browser consumer. Next.js guidance supports server authorization and minimal client-visible contracts; OWASP LLM05 supports…
Related cases
- Instagram client configuration exposed an application credential
Meta · Information exposure and response privacy · USD 30,000
- Facebook error responses exposed unintended application data
Meta (Facebook) · Information exposure and response privacy · USD 65,000
- Support integration exposed internal Confluence documentation
HackerOne · Authorization and tenant boundaries · USD 12,500
- GraphQL object authorization exposed private-program metadata
HackerOne · Authorization and tenant boundaries · USD 25,000
Sources
- We’re Running Hai Insight Agent on Our Own Bug Bounty Program – See it in ActionCrystal Hazen / HackerOne · reviewed 2026-10-03
- Vulnerability Disclosure StandardsHackerOne · reviewed 2026-10-02
- HackerOne terms and disclosure guidelines in official reseller GSA contract attachment, Exhibit CHackerOne / Carahsoft (contract attachment) · reviewed 2026-10-02
- Public report 3000510: private user attributes exposed in report serializationHackerOne and avinash_ · reviewed 2026-10-03
Record reviewed 2026-10-03. Snapshot af2809c308fc. Open the complete JSON contract.