The conceptual model
Cases and references behind the model
Sources
- nextjs.orgPrimary source
- genai.owasp.orgPrimary source
- www.hackerone.comPrimary source
Record reviewed 2026-10-03. Snapshot af2809c308fc. Open the complete JSON contract.
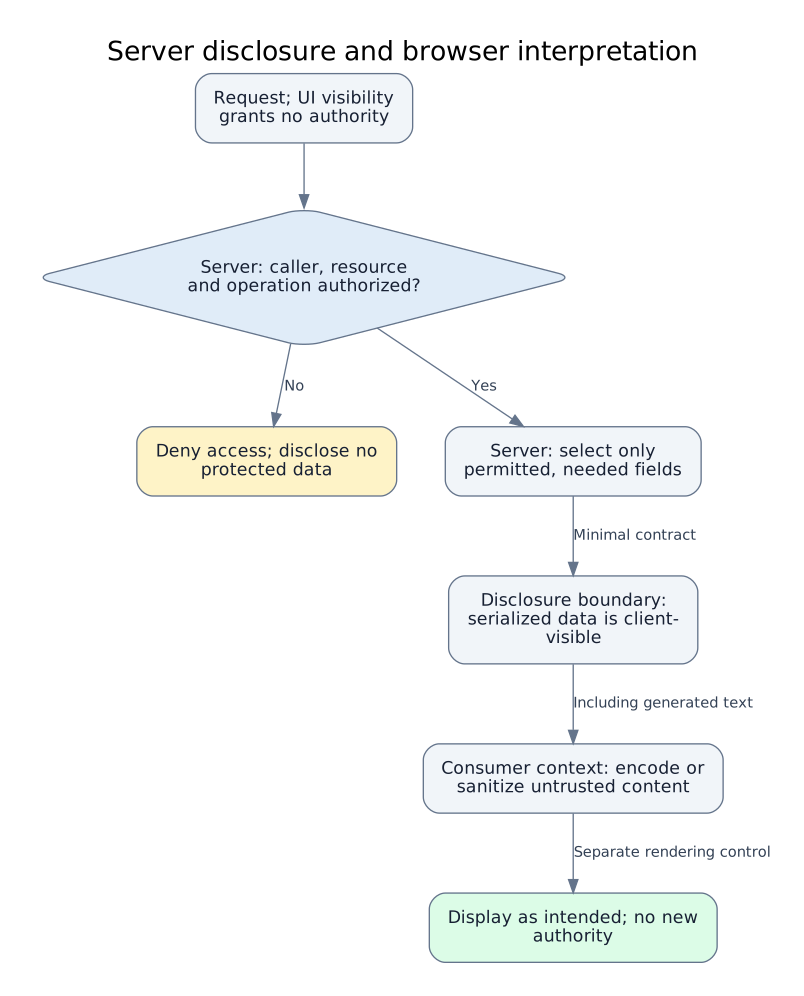
Editorial conceptual model: assumes an application with server-side privileged data and a browser consumer. Next.js guidance supports server authorization and minimal client-visible contracts; OWASP LLM05 supports treating generated text as untrusted at each consumer. The linked HackerOne Rails case illustrates why serialization needs an explicit disclosure boundary; it is not evidence of Next.js or an LLM integration. The arrows show defensive responsibilities, not a framework execution trace. Context-aware encoding or sanitization belongs where the output context is known, including server rendering; the lower steps do not imply exclusively client-side execution. Rendering safety cannot replace permission checks, and authorized disclosure does not make content safe to interpret.
Record reviewed 2026-10-03. Snapshot af2809c308fc. Open the complete JSON contract.
Library synced 2026-11-18 · cases last reviewed 2026-10-05
af2809c308fc · JSON exports & schemas · CC BY 4.0 content / MIT software
| / | Focus search on this page |
| Ctrl K | Search everything (command palette) |
| 1-9 | Library, Generator, Playbooks, Gadgets, Checklists, Payloads, Bypasses, Utilities, Reports |
| 0 | AI / MCP connector |
| j / k | Move selection down / up |
| Enter | Expand / open selected |
| c | Copy primary command of selected |
| f | Toggle favorite on selected tool |
| Esc | Clear search / close |