How to use this reference
Map each output consumer in an owned AI application to its validation and encoding contract. Prefer parameterized database operations and context-aware encoding, with monitoring and browser policy controls as supplementary layers.
Before reading
- Basic LLM application data flow
- Context-sensitive encoding and separation of data from executable interpretation
Context and limits
- The 2025 designation is an edition identifier, not a verified publication date.
- The source contains attack scenarios; this record retains only trust-boundary and remediation concepts.
- This category describes possible failure modes rather than current exposure of a particular product.
Related visual models
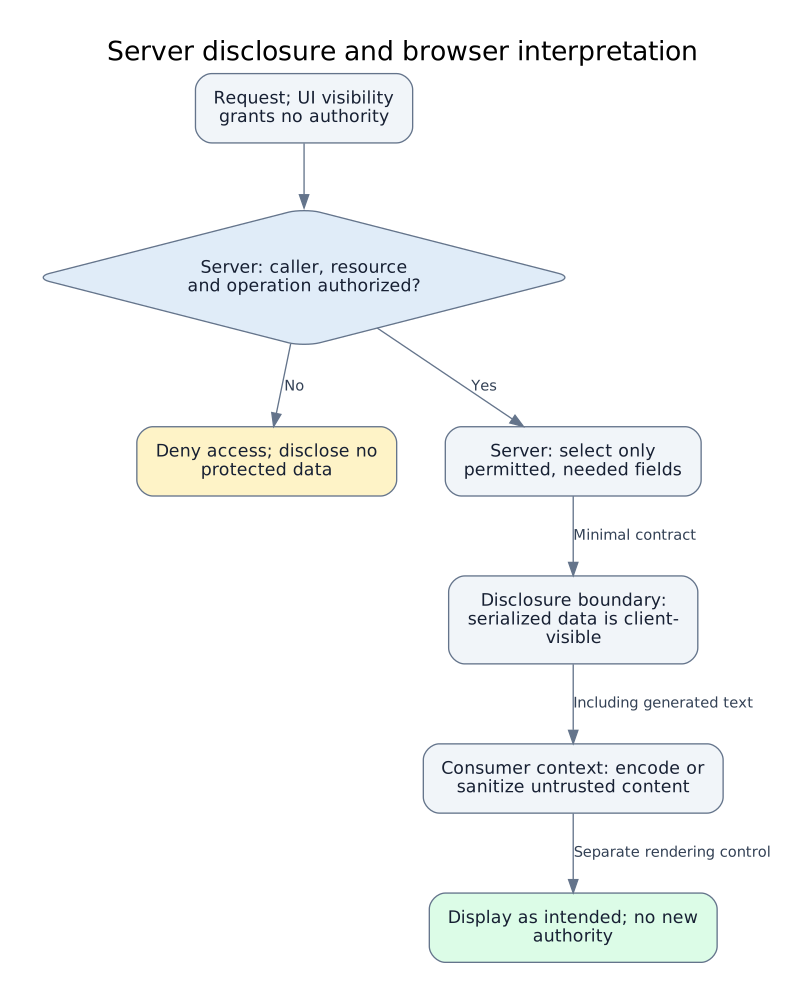
Server disclosure and browser interpretation
Editorial conceptual model: assumes an application with server-side privileged data and a browser consumer. Next.js guidance supports server authorization and minimal client-visible contracts; OWASP LLM05 supports…
Reviewed 2026-10-03Read
Sources and provenance
- LLM05:2025 Improper Output Handling OWASP Gen AI Security Project · reviewed 2026-10-03
Record reviewed 2026-10-03. Snapshot 53796974ace8. Open the complete JSON contract.