How to use this reference
Editorial lesson: authorization on a parent object cannot authorize every object reachable from it. Define response contracts that preserve both per-document access and field visibility during expansion. The maintainer advisory identifies patched releases 15.104.0 and 16.14.0; it does not describe the patch implementation.
Before reading
- Basic API access-control concepts
- Familiarity with server-side data processing
Context and limits
- Requires a readable parent document whose expanded links reach records the caller cannot otherwise access; it does not establish unrestricted access to every document.
- The publication explains the code-level disclosure mechanism but supplies no customer incident or measured data-loss evidence. Do not infer write access or account takeover.
- Reported January 19, 2026; maintainer advisory published April 7; detailed research published April 24. Fix-release dates were not established by the reviewed sources.
- The byline is Man Yue Mo. Discovery is credited to GitHub Security Lab Taskflow Agent, with human review by Peter Stöckli and Man Yue Mo. Learning prerequisites are editorial.
Related visual models
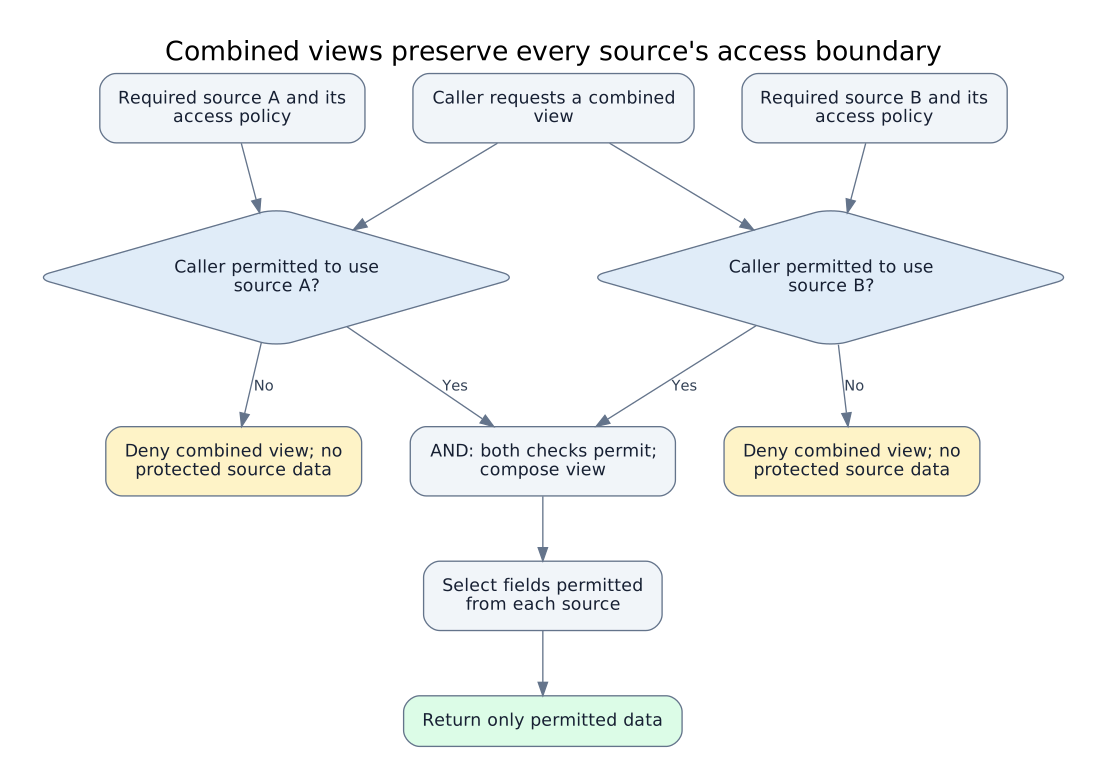
Combined views preserve every source's access boundary
Original conceptual model for a view that requires multiple independently protected sources. Permission to use one source cannot authorize another source. The convergence is an AND requirement: both source decisions…
Reviewed 2026-10-04
Sources
- GHSL-2026-012: Unauthorized Data Exposure via REST API Link Expansion in Frappe - CVE-2026-39351GitHub Security Lab · reviewed 2026-10-03
- Unrestricted Doctype access via API exploitFrappe · reviewed 2026-10-03
Record reviewed 2026-10-03. Snapshot af2809c308fc. Open the complete JSON contract.