Conceptual model · 1 min read
Combined views preserve every source's access boundary
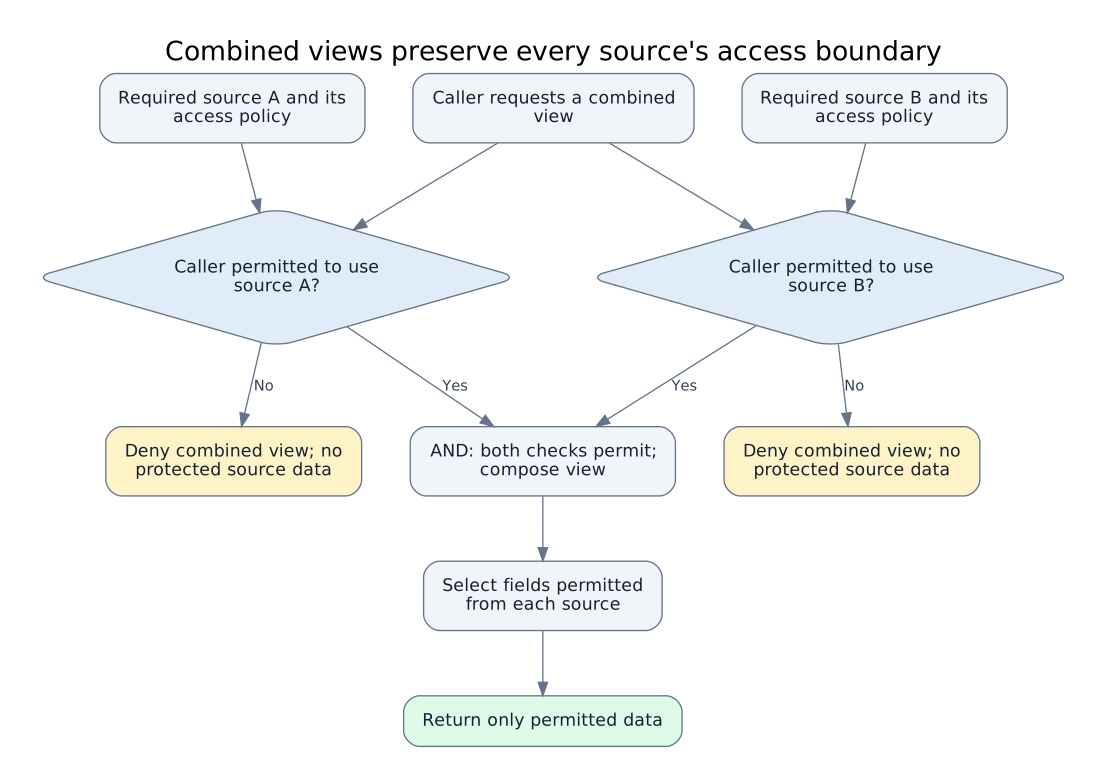
Original conceptual model for a view that requires multiple independently protected sources. Permission to use one source cannot authorize another source. The convergence is an AND requirement: both source decisions must permit the requesting actor before composition. GitHub’s comparison disclosure supports the cross-repository boundary; Frappe’s linked-document disclosure supports independent document permissions and field selection. OWASP provides the general per-request and deny-by-default guidance. The graph assumes an all-or-nothing response contract. Applications supporting partial results need a separately specified non-disclosing omission policy. Field selection remains a distinct requirement even when every source check permits access. This is not either vendor’s architecture or patch implementation. Snapshot consistency, permission-change races and inference from combined values are outside this model.