Root cause
GitHub identifies an access-control failure in cross-repository comparison (vendor-report; vendor-release). Permission to read one repository did not grant permission to see code from another repository in the comparison. The user needed existing repository access and prior knowledge of private-repository references; this was not unrestricted anonymous browsing. The general lesson is to check access to every source used in a combined view. The vendor does not disclose how the access checks were implemented.
Demonstrated impact
The vendor confirms limited code disclosure from an otherwise unauthorized repository (vendor-report; vendor-release). The public summary does not establish complete repository extraction, write access, account takeover, or exploitation in the wild; those outcomes must not be inferred from the broader report title.
What to check for
- Editorial design lesson: authorize every contributing source under the requesting actor before returning a combined or derived view.
- Editorial review objective: ensure that permission to access one repository never substitutes for permission to read another repository’s content.
- GitHub lists historical fixes in GHES 3.14.17, 3.15.12, 3.16.8 and 3.17.5 (vendor-report). These are historical remediation evidence, not current upgrade recommendations; the 3.17 documentation now marks that release series unsupported (vendor-release).
Award and evidence
How the award was verified, and what the record does not establish
One report award; cash receipt is unverified. USD is inferred from HackerOne’s platform-wide payment policy reviewed in October 2026, later than the August 2025 award; that context does not independently establish settlement.
- Public report content supplies a vendor summary, not implementation-level patch details or a complete demonstration transcript.
- GitHub.com deployment timing and exploitation-in-the-wild status are not established by the reviewed sources.
- Release availability, report resolution and detailed publication have different dates.
- Cash receipt is unverified; later platform-wide USD policy is contextual denomination evidence.
Timeline
- Published
- 2025-09-23explicit · Detailed report disclosure event, activity-37054322.
- Public Disclosure
- 2025-08-25explicit · Vendor advisory in Enterprise Server 3.17.5 release notes preceded the detailed report.
- Reported
- 2025-05-03explicit
- Awarded
- 2025-08-26explicit
- Fixed
- 2025-08-25explicit · Public GHES 3.17.5 release. Report Resolved status is August 26; GitHub.com deployment timing is not established.
Related visual models
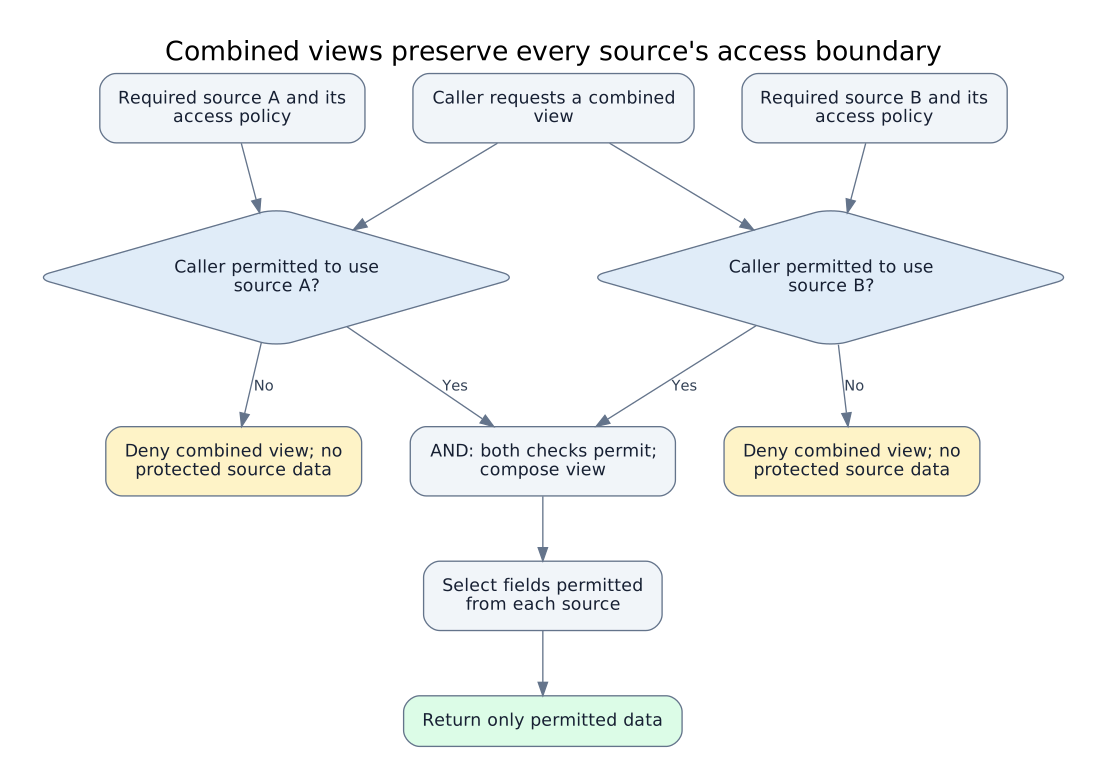
Combined views preserve every source's access boundary
Original conceptual model for a view that requires multiple independently protected sources. Permission to use one source cannot authorize another source. The convergence is an AND requirement: both source decisions…
Related cases
- Google Mamba temporary outputs lacked access isolation
Google · Authorization and tenant boundaries · USD 37,604.40
- Google Firefly confused worker authority and storage boundaries
Google · Authorization and tenant boundaries · USD 60,000
- Google Application Integration mixed resource and service authority
Google · Authorization and tenant boundaries · USD 75,000
- Google support API exposed customer and agent data
Google · Authorization and tenant boundaries · USD 14,337
- GitHub package-source trust allowed dependency confusion
GitHub · Software supply-chain security · USD 20,000
- GitHub unsafe reflection crossed method and credential boundaries
GitHub · Injection and untrusted input · USD 75,000
Sources
- GitHub HackerOne report 3124517GitHub security team and furbreeze · reviewed 2026-10-03
- GitHub Enterprise Server 3.17.5 release notesGitHub · reviewed 2026-10-03
- Vulnerability Disclosure Standards: Bug Bounty payment denominationHackerOne · reviewed 2026-10-03
Record reviewed 2026-10-03. Snapshot af2809c308fc. Open the complete JSON contract.