Root cause
Insufficient separation between user-supplied driver code and a privileged shared service identity.
Demonstrated impact
Researchers demonstrated execution and observed service-account access across many compute instances. Broader customer-project compromise was claimed, not independently verified.
Lessons for review
- Isolate extension execution from service credentials.
- Scope delegated identities to the minimum tenant and resource set.
- Distinguish observed permissions from untested downstream impact.
Award and evidence
One report: USD 5,000 base doubled by a collaboration grant. The separate Dataprep finding in this article received no cash bounty. USD denomination follows official Google program context; recipient split and cash settlement unknown.
Full researcher article read in the cloud browser after text retrieval returned only the page shell. Award paragraph isolated from the unrelated unrewarded finding.
- Award is researcher-reported; no cash receipt or per-contributor split is supplied.
- Exact original-report, award, payment, fix and first-disclosure dates are unavailable.
- Broad cross-customer impact is the researcher’s assessment, not evidence of customer-data extraction.
Recorded timeline
- Published
- 2025-05-04explicit
Related visual models
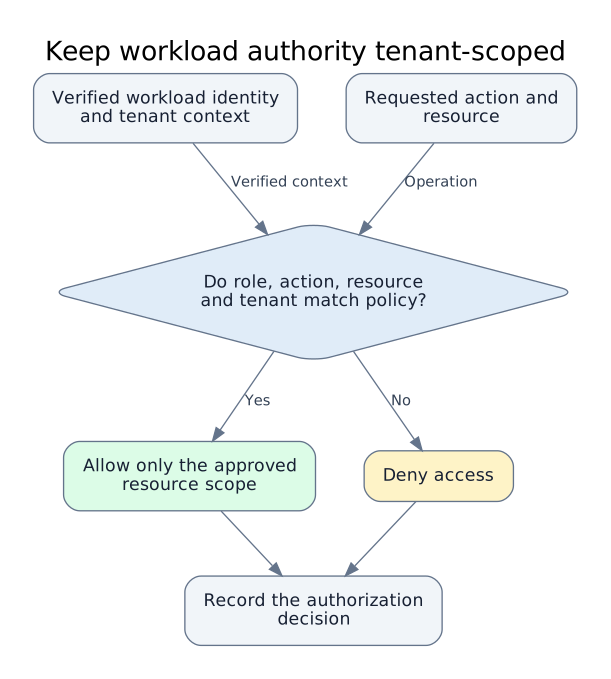
Keep workload authority tenant-scoped
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Sources and provenance
- Two RCEs in Google Cloud products and Nike Air Max 90s Sivanesh Ashok · reviewed 2026-10-02
- VRP news from Nullcon: Google web VRP USD denomination Josh Armour / Google · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot d5550c789111. Open the complete JSON contract.