vulns.co
/
GKData.io MCP

Conceptual model · 1 min read

Keep workload authority tenant-scoped

Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.

The conceptual model
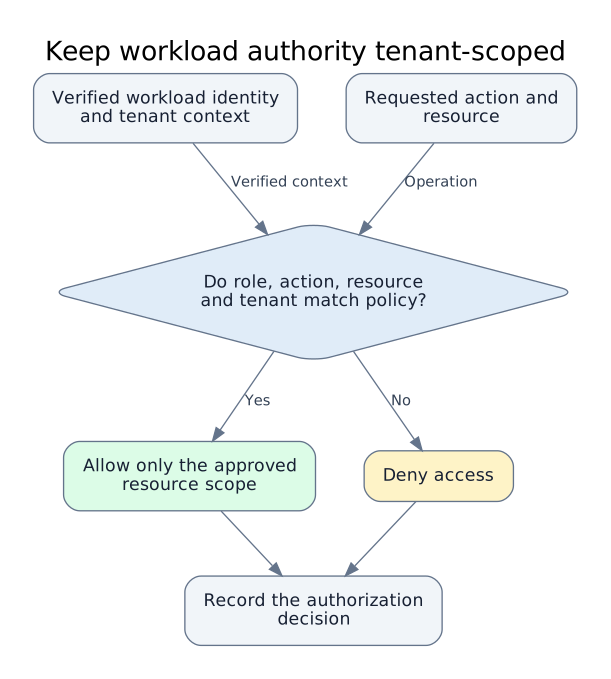
A verified workload identity and a requested operation enter an independent authorization decision. Policy checks the role, action, resource and tenant together. Only the approved resource scope is allowed; other requests are denied. Both decisions produce an audit record.

Cases and references behind the model

Sources and provenance

  1. sectricity.com Primary source
  2. stazot.com Primary source
  3. docs.aws.amazon.com Primary source

Record reviewed 2026-10-02. Snapshot d5550c789111. Open the complete JSON contract.

GitHub snapshot 2026-10-04

d5550c789111 · JSON exports & schemas · CC BY 4.0 content / MIT software