Root cause
An exposed service identity had unnecessarily broad access to secrets, with downstream integration credentials extending the potential impact into private source repositories. Apply strong service authentication, minimize identity permissions, and separate trust between integrations.
Demonstrated impact
Researchers report potential read/write access to 507 private repositories; their write-up says they confirmed the count and did not clone or browse repository contents.
Lessons for review
- Require authenticated, explicitly authorized access to service identities.
- Constrain secret access and integration privileges to the minimum required.
- Document exposure without copying private customer or source data.
Award and evidence
Use the $150,000 base award. The headline says $157K, but the stated 5% bonus would imply $157,500; exact total is not asserted. USD normalization of the dollar-denominated Meta award; the reproduced individual message uses $.
Primary public sources read; reward distinguished from maximums and aggregates. Historical defensive summary only; no vulnerability testing performed.
- Headline states $157K, while $150,000 plus 5% arithmetically equals $157,500; use the undisputed $150,000 base and preserve this discrepancy
- Vendor response is reproduced by the researcher organization, not independently hosted by Meta
- The exposed Grafana dashboard was a discovery signal, not established as the underlying rewarded vulnerability
Recorded timeline
- Reported
- 2026-03-21explicit
- Awarded
- 2026-04-29explicit
- Mitigated
- 2026-03-23explicit · Triaged and mitigated according to the researcher timeline.
- Published
- 2026-05-28explicit
Related visual models
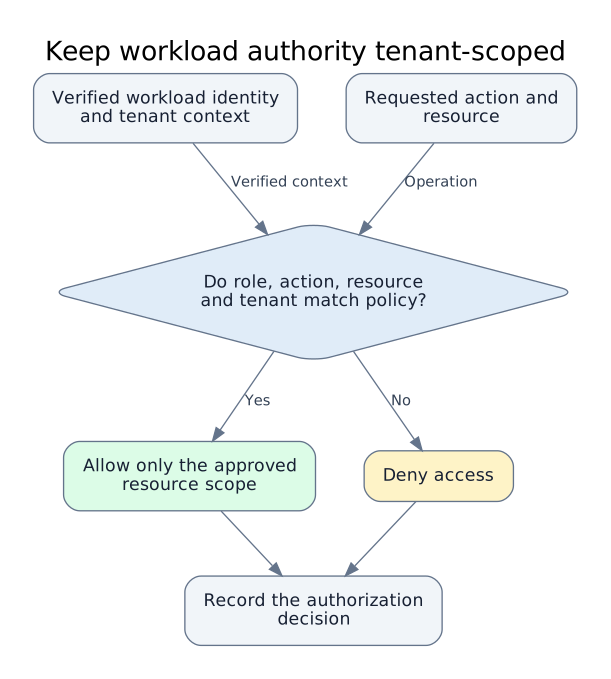
Keep workload authority tenant-scoped
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Sources and provenance
- Meta service-identity exposure amplified by excessive secret access Preben Ver Eecke, Sectricity · reviewed 2026-10-02
- Supporting primary disclosure source Preben Ver Eecke, Sectricity · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot d5550c789111. Open the complete JSON contract.