How to use this reference
Compare an owned workload’s documented identity lifecycle and minimum permission needs with the guide, recording unnecessary access for review.
Before reading
- Basic understanding of cloud workloads, roles, and identity policies
- Familiarity with authentication versus authorization
Context and limits
- AWS-managed policies may need further narrowing for a specific workload.
- Organization-level guardrails constrain permissions; they do not grant access by themselves.
Related visual models
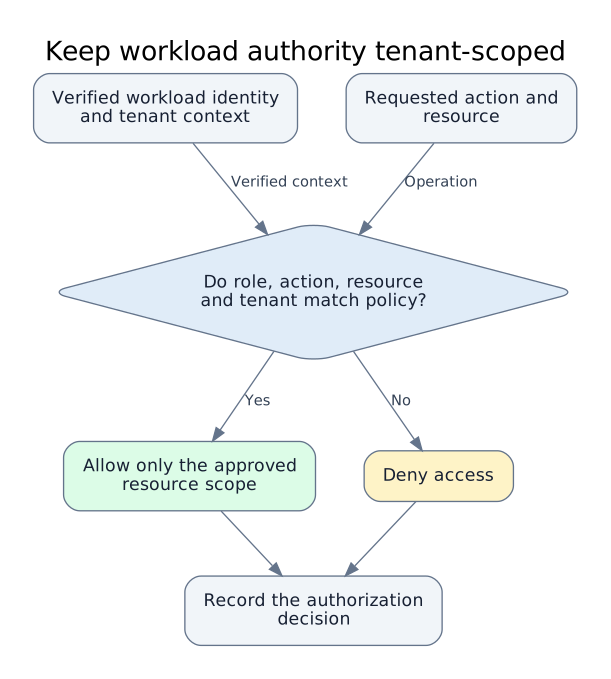
Keep workload authority tenant-scoped
Editorial conceptual model derived from the linked cases and official guidance; not a vendor architecture diagram or an exploitation sequence.
Reviewed 2026-10-02
Sources
- Temporary workload credentials, least privilege, access cleanup, policy validation, and permissions guardrailsAmazon Web Services · reviewed 2026-10-02
Record reviewed 2026-10-02. Snapshot af2809c308fc. Open the complete JSON contract.