How to use this reference
Using synthetic events in an owned application, review whether records can explain a decision without exposing credentials or personal data. Document correlation gaps, timestamp uncertainty and what the logs cannot prove.
Before reading
- Basic familiarity with application events and structured logs
- Understanding of sensitive-data handling and access controls
Context and limits
- Logging does not automatically provide independent proof or non-repudiation.
- Collection and retention must match the authorized purpose; more recorded data is not necessarily better evidence.
Related visual models
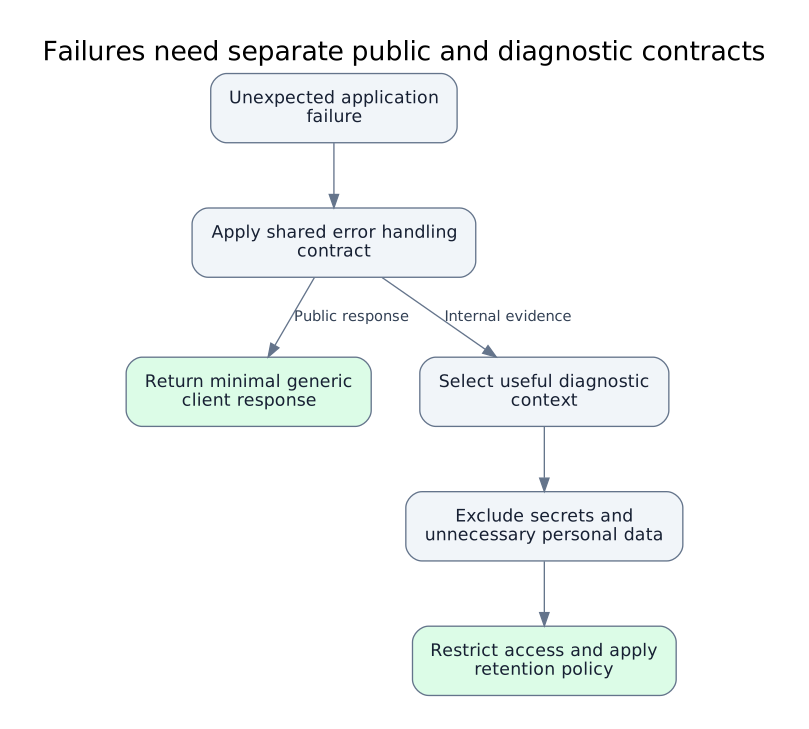
Failures need separate public and diagnostic contracts
Editorial conceptual model derived from the Facebook error-response case and OWASP error-handling and logging guidance. The case establishes unintended response disclosure and broader framework remediation; diagnostic…
Reviewed 2026-10-03
Sources
- OWASP Logging: trustworthy and minimal application evidenceOWASP Cheat Sheet Series · reviewed 2026-10-03
Record reviewed 2026-10-03. Snapshot af2809c308fc. Open the complete JSON contract.