Parsers, archives, and fail-open
Review file and document processing as a chain of bounded parsing, typed validation, storage, and authorized action.
This is the complete downloadable file. Open plain text ↗
---
name: parser
description: "Review file and document processing as a chain of bounded parsing, typed validation, storage, and authorized action."
---

# Parsers, archives, and fail-open

Review file and document processing as a chain of bounded parsing, typed validation, storage, and authorized action.

Defensive study and review of artifacts supplied by their owner. Record missing evidence as an open question.

## Bring to the review

- Parser and upload design
- Accepted file and archive policy
- Owned sample artifacts and unit tests

## Review guide

### 1. Define accepted meaning

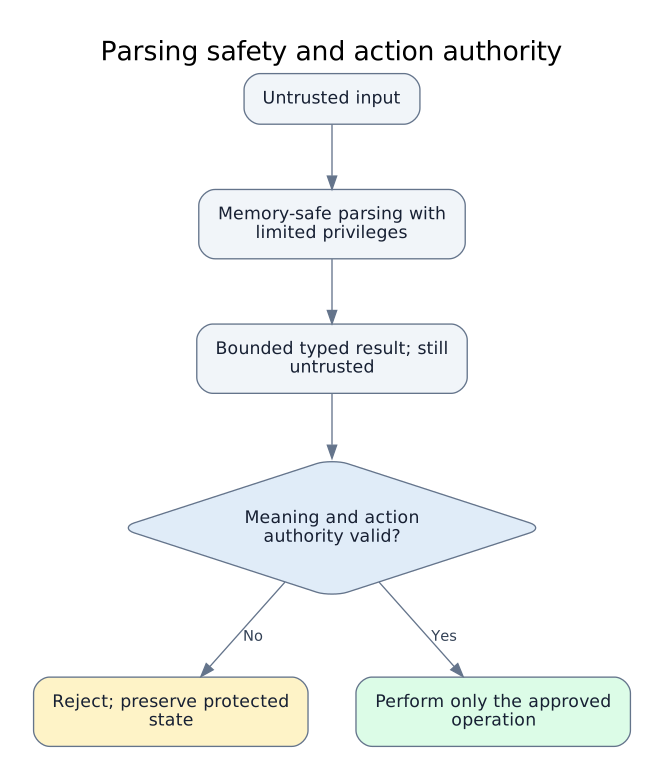
Specify supported formats, size and complexity budgets, encoding rules, and the safe typed result each parser may produce.

### 2. Keep parsing contained

Run processing with minimal privileges and isolate it from sensitive filesystem, network, and interpreter authority.

### 3. Validate after parsing

Treat parsed metadata and paths as untrusted until they satisfy an application-specific authorization and storage policy.

### 4. Review failure behavior

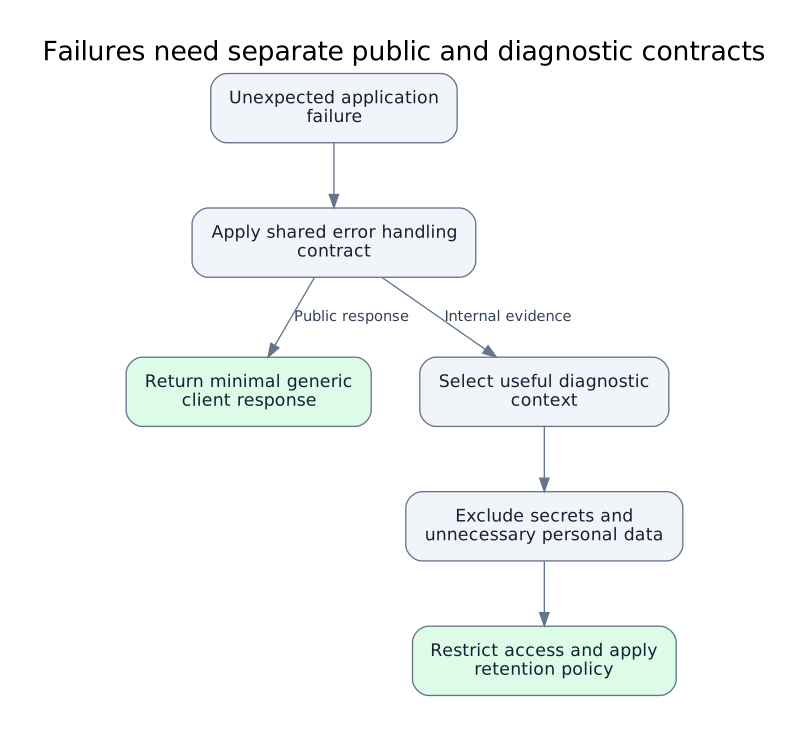
Ensure malformed or unsupported input produces a bounded rejection without partial state or public diagnostics.

## What to produce

- Format acceptance contract
- Processing isolation notes
- Failure-handling tests

## Common mistakes

- Trusting declared content type
- Letting parsed paths select storage targets
- Converting parser errors into permissive behavior

## Reading and source context

### Resources

- [Chromium Rule of Two: input trust, memory safety and privilege](https://vulns.co/research/resources/chromium-rule-of-two-input-isolation/)
- [pypdf: bound repeated work when reading embedded attachments](https://vulns.co/research/resources/pypdf-2026-attachment-processing-cost-boundary/)
- [Error Handling Cheat Sheet](https://vulns.co/research/resources/owasp-error-response-data-minimization/)

### Diagrams

- [Parsing safety and action authority](https://vulns.co/research/diagrams/parsing-safety-action-authority/)
- [Failures need separate public and diagnostic contracts](https://vulns.co/research/diagrams/error-diagnostic-disclosure-boundary/)

### Reports

- [V8 optimized object handling retained invalid type assumptions](https://vulns.co/research/reports/google-chrome-v8-type-consistency-2025/)
- [Redis Lua object lifetime failure crossed the scripting boundary](https://vulns.co/research/reports/redis-lua-object-lifetime-isolation-2025/)
- [Facebook error responses exposed unintended application data](https://vulns.co/research/reports/facebook-error-response-data-isolation-2019/)

## Provenance

Editorial guide by vulns.co / GK Data. Updated 2026-10-11.
Library snapshot: 2026-10-04; commit d5550c7891119cf1379e235721541c947850a3b3.
The guide is an editorial synthesis. Linked records preserve their own sources and review dates.

Reader: https://vulns.co/skills/parser/
The review
What to look for
Defensive study and review of artifacts supplied by their owner. Record missing evidence as an open question.
Define accepted meaning
Specify supported formats, size and complexity budgets, encoding rules, and the safe typed result each parser may produce.
Keep parsing contained
Run processing with minimal privileges and isolate it from sensitive filesystem, network, and interpreter authority.
Validate after parsing
Treat parsed metadata and paths as untrusted until they satisfy an application-specific authorization and storage policy.
Review failure behavior
Ensure malformed or unsupported input produces a bounded rejection without partial state or public diagnostics.
What to produce
- Format acceptance contract
- Processing isolation notes
- Failure-handling tests
Common mistakes
- Trusting declared content type
- Letting parsed paths select storage targets
- Converting parser errors into permissive behavior
Continue the study
Reading & source context
Editorial notes above connect these references. Open each record for its original source and review date.
Visual models
Connected disclosures
From the field toolkit
Guide by GK Data · Research snapshot 2026-10-04.
Sources and review dates are preserved in the library provenance.