Provisioning and invites
Review invites, directory sync, and provisioning as high-authority lifecycle operations with tenant, role, and approval checks.
This is the complete downloadable file. Open plain text ↗
---
name: provision
description: "Review invites, directory sync, and provisioning as high-authority lifecycle operations with tenant, role, and approval checks."
---

# Provisioning and invites

Review invites, directory sync, and provisioning as high-authority lifecycle operations with tenant, role, and approval checks.

Defensive study and review of artifacts supplied by their owner. Record missing evidence as an open question.

## Bring to the review

- Provisioning protocol configuration
- Organization and role model
- Approved lifecycle events

## Review guide

### 1. Map ownership

Bind each provider, invitation, group mapping, and lifecycle event to a specific organization owner and approved administrator.

### 2. Constrain role changes

Require explicit policy for role assignment, deprovisioning, and cross-organization moves; do not infer authority from profile edits.

### 3. Review durable links

Validate that directory attributes and external identities retain provenance and cannot silently rebind an account.

### 4. Verify revocation

Confirm disabled users, removed memberships, and revoked providers lose access across all active interfaces.

## What to produce

- Provisioning authority map
- Role-change policy
- Deprovisioning verification notes

## Common mistakes

- Treating an invite as blanket authority
- Allowing ownerless configuration
- Leaving stale group access after deprovisioning

## Reading and source context

### Resources

- [Better Auth SCIM: absent ownership must not grant shared authority](https://vulns.co/research/resources/better-auth-2026-scim-ownerless-provider-authority/)
- [n8n: directory-attribute authority in durable account linking](https://vulns.co/research/resources/n8n-2026-ldap-account-linking-authority/)
- [Umbraco: editing an account does not authorize assigning every role](https://vulns.co/research/resources/umbraco-2026-group-assignment-authority/)

### Diagrams

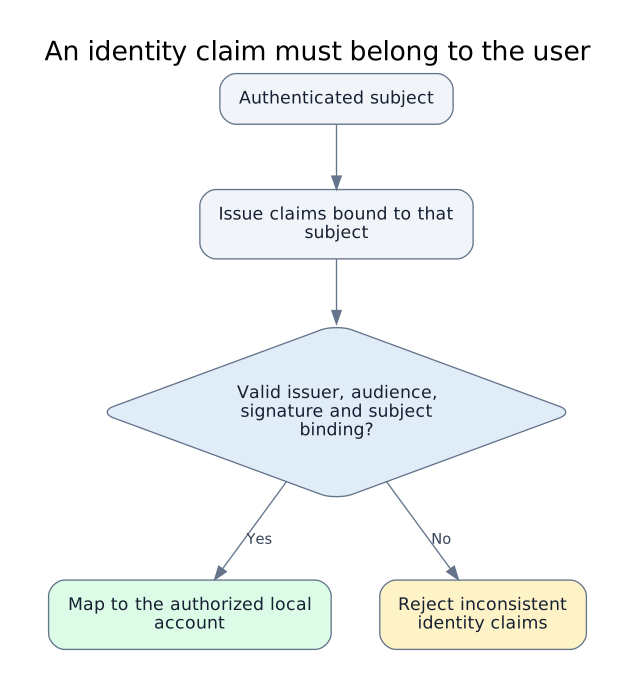
- [An identity claim must belong to the user](https://vulns.co/research/diagrams/identity-claim-binding/)
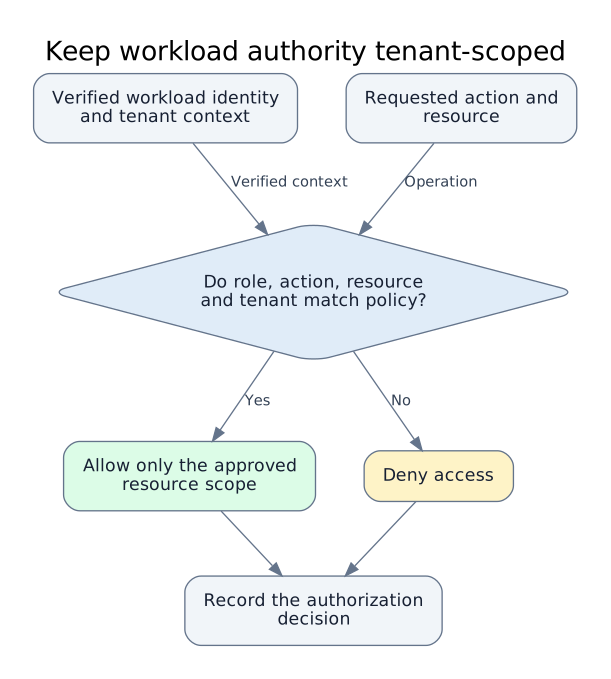
- [Keep workload authority tenant-scoped](https://vulns.co/research/diagrams/workload-identity-tenant-scope/)

### Reports

- [Sign in with Apple failed to bind identity claims to the authenticated user](https://vulns.co/research/reports/apple-sign-in-identity-claim-binding-2020/)
- [GitHub OAuth consent failed across request-method semantics](https://vulns.co/research/reports/github-oauth-method-semantics-2019/)
- [Meta service-identity exposure amplified by excessive secret access](https://vulns.co/research/reports/meta-service-identity-secrets-trust-boundary-2026/)

## Provenance

Editorial guide by vulns.co / GK Data. Updated 2026-10-11.
Library snapshot: 2026-10-04; commit d5550c7891119cf1379e235721541c947850a3b3.
The guide is an editorial synthesis. Linked records preserve their own sources and review dates.

Reader: https://vulns.co/skills/provision/
The review
What to look for
Defensive study and review of artifacts supplied by their owner. Record missing evidence as an open question.
Map ownership
Bind each provider, invitation, group mapping, and lifecycle event to a specific organization owner and approved administrator.
Constrain role changes
Require explicit policy for role assignment, deprovisioning, and cross-organization moves; do not infer authority from profile edits.
Review durable links
Validate that directory attributes and external identities retain provenance and cannot silently rebind an account.
Verify revocation
Confirm disabled users, removed memberships, and revoked providers lose access across all active interfaces.
What to produce
- Provisioning authority map
- Role-change policy
- Deprovisioning verification notes
Common mistakes
- Treating an invite as blanket authority
- Allowing ownerless configuration
- Leaving stale group access after deprovisioning
Continue the study
Reading & source context
Editorial notes above connect these references. Open each record for its original source and review date.
Visual models
Connected disclosures
From the field toolkit
Guide by GK Data · Research snapshot 2026-10-04.
Sources and review dates are preserved in the library provenance.