Cloud object storage
Review cloud storage and service access through attributable ownership, least privilege, destination policy, and auditable configuration.
This is the complete downloadable file. Open plain text ↗
---
name: cloud
description: "Review cloud storage and service access through attributable ownership, least privilege, destination policy, and auditable configuration."
---

# Cloud object storage

Review cloud storage and service access through attributable ownership, least privilege, destination policy, and auditable configuration.

Defensive study and review of artifacts supplied by their owner. Record missing evidence as an open question.

## Bring to the review

- Cloud account and resource inventory
- IAM and storage policies
- Approved architecture and egress requirements

## Review guide

### 1. Establish ownership

Tie each bucket, service identity, and integration to a documented account, environment, and responsible owner before drawing conclusions.

### 2. Review effective policy

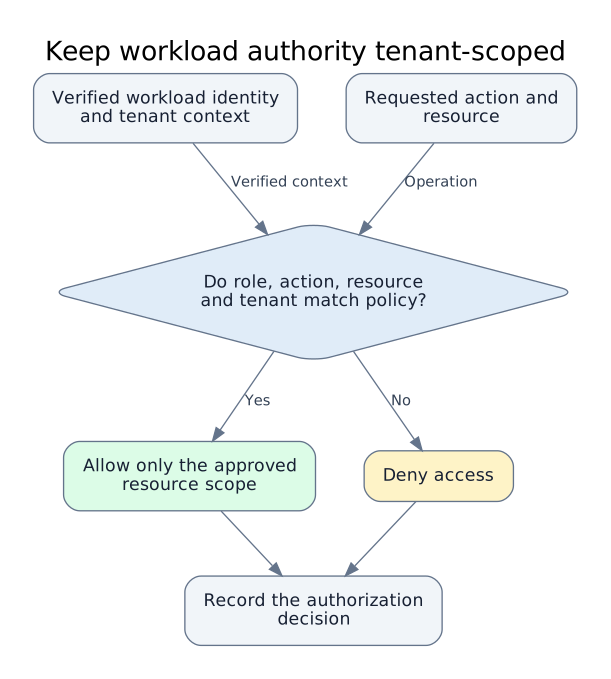
Evaluate identity, resource, network, and conditional policies together for the exact action and tenant context.

### 3. Constrain service egress

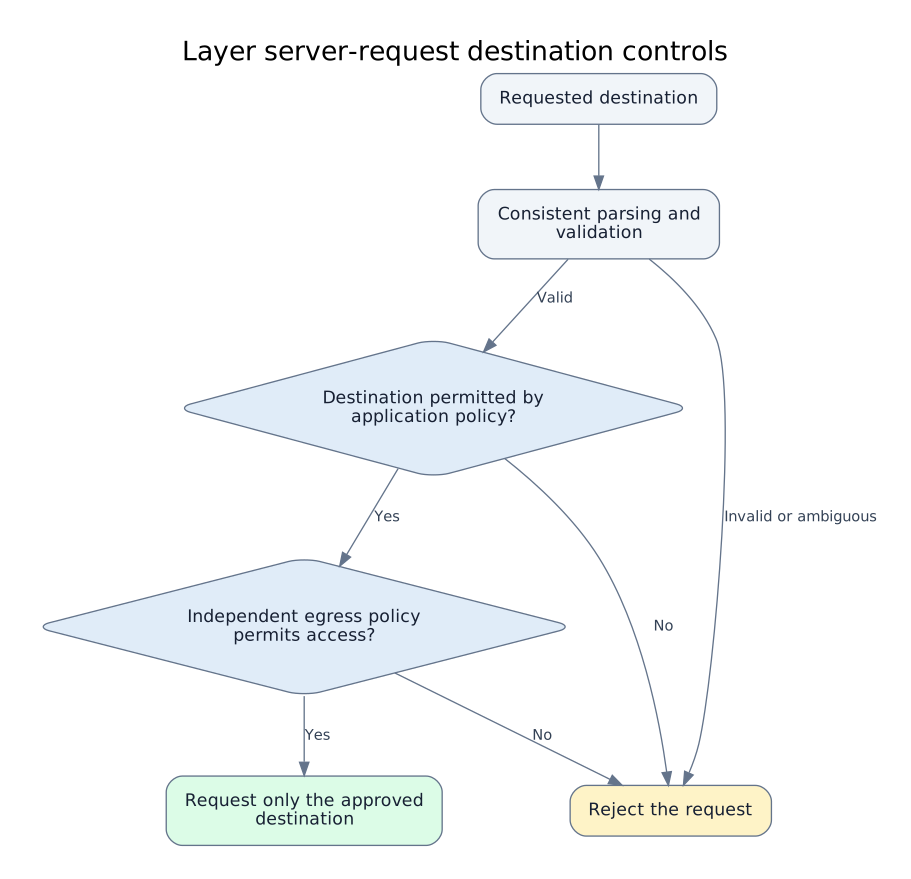
Apply an explicit destination policy plus independent network controls for server-side requests.

### 4. Audit change paths

Ensure configuration changes, public sharing, and credential rotation leave reviewable records and safe defaults.

## What to produce

- Attributed asset inventory
- Effective-permission review
- Egress and audit controls

## Common mistakes

- Calling an internet-visible asset owned without attribution
- Reviewing IAM policies in isolation
- Using a network control as the only destination check

## Reading and source context

### Resources

- [AWS IAM security best practices for workload identities](https://vulns.co/research/resources/aws-iam-machine-identity-best-practices/)
- [OWASP Server-Side Request Forgery Prevention](https://vulns.co/research/resources/owasp-server-request-destination-boundaries/)
- [NIST SP 800-190: Application Container Security Guide](https://vulns.co/research/resources/nist-sp-800-190-container-isolation-guide/)

### Diagrams

- [Layer server-request destination controls](https://vulns.co/research/diagrams/server-request-destination-policy/)
- [Keep workload authority tenant-scoped](https://vulns.co/research/diagrams/workload-identity-tenant-scope/)

### Reports

- [Shopify Exchange screenshot service crossed internal boundaries](https://vulns.co/research/reports/shopify-exchange-request-isolation-2019/)
- [Meta service-identity exposure amplified by excessive secret access](https://vulns.co/research/reports/meta-service-identity-secrets-trust-boundary-2026/)
- [Actifio driver execution exposed excessive shared-service authority](https://vulns.co/research/reports/google-actifio-driver-service-identity-isolation-2025/)

## Provenance

Editorial guide by vulns.co / GK Data. Updated 2026-10-11.
Library snapshot: 2026-10-04; commit d5550c7891119cf1379e235721541c947850a3b3.
The guide is an editorial synthesis. Linked records preserve their own sources and review dates.

Reader: https://vulns.co/skills/cloud/
The review
What to look for
Defensive study and review of artifacts supplied by their owner. Record missing evidence as an open question.
Establish ownership
Tie each bucket, service identity, and integration to a documented account, environment, and responsible owner before drawing conclusions.
Review effective policy
Evaluate identity, resource, network, and conditional policies together for the exact action and tenant context.
Constrain service egress
Apply an explicit destination policy plus independent network controls for server-side requests.
Audit change paths
Ensure configuration changes, public sharing, and credential rotation leave reviewable records and safe defaults.
What to produce
- Attributed asset inventory
- Effective-permission review
- Egress and audit controls
Common mistakes
- Calling an internet-visible asset owned without attribution
- Reviewing IAM policies in isolation
- Using a network control as the only destination check
Continue the study
Reading & source context
Editorial notes above connect these references. Open each record for its original source and review date.
Visual models
Connected disclosures
From the field toolkit
Guide by GK Data · Research snapshot 2026-10-04.
Sources and review dates are preserved in the library provenance.